2026-10-10
Your source for daily security alerts from some of the best experts in the world.
Find the problems, secure your systems now!
Get these alerts in your inbox every morning. Subscribe
A vulnerability has been discovered in Citrix NetScaler Application Delivery Controller (ADC) and Citrix NetScaler Gateway that could allow for remote code execution. Citrix NetScaler ADC (Application Delivery Controller) is an enterprise networking platform and traffic management device designed to optimize, secure, and accelerate the delivery of web and cloud applications. Successful exploitation of the most severe of these vulnerabilities could allow attackers to gain remote code execution (RCE) on targeted devices or trigger a denial-of-service state that can cause crashes. To be vulnerable, NetScaler ADC and NetScaler Gateway appliances must be configured as a Security Assertion Markup Language (SAML) Identity Provider (IdP) or Service Provider (SP).
10/09TOCFBI Arrests Founder of Ransomware Negotiation Firm Agents with the Federal Bureau of Investigation (FBI) on Thursday arrested the co-founder of a Canadian cybersecurity firm in connection with an investigation into the ShinyHunters hacking group that recently relieved the FBI of sensitive data on thousands of agents, multiple sources tell KrebsOnSecurity.10/07TOCShinyHunters Extorted Boeing Spin-off Prior to Arrests A teenager from Amman, Jordan suspected of leading the prolific data theft and extortion group ShinyHunters has been detained and is reportedly cooperating with the FBI to identify other members of the hacking gang. KrebsOnSecurity has learned that the suspect, who uses the hacker handle “Rey,” was detained as ShinyHunters was in the process of extorting a business unit recently divested by the global aerospace company Boeing, which manufactures the fleet of planes used by the employer of Rey’s father — Royal Jordanian Airlines.
Hacker News
10/10TOCAnthropic Cuts Live Internet Access for Internal AI Tests After Claude… Anthropic on Friday said it’s cutting off live internet access for all its internal evaluations following the discovery of new incidents in which its artificial intelligence (AI) models exhibited misaligned behavior and targeted real websites.
The AI company said it identified four broad categories of unintended model actions during evaluations and internal use of Claude –
Claude Mythos10/09TOCCredential-Stealing GitHub Actions Workflows Planted in Tens of Thousa… Cybersecurity researchers have disclosed details of an ongoing credential-theft campaign that has compromised two high-profile open-source maintainer accounts to push a malicious workflow into over 340 repositories.
“Using the account of Takashi Kitao, author of the 18,400-star game engine pyxel, the attacker pushed a malicious workflow to 27 repositories starting at 13:20 UTC,” StepSecurity10/09TOCFBI Arrests Another ShinyHunters Suspect Reportedly Involved in Its Jo… The FBI has arrested another suspected co-conspirator of ShinyHunters, FBI Director Kash Patel said on October 9 in a post on X.
ShinyHunters is the extortion group that said in September it had breached the FBI’s jobs portal and stolen sensitive data on almost all FBI agents and job applicants. The FBI has not named the suspect, and no charges have been made public.
The10/09TOCP7 DarkSword iOS Exploit Kit Adds Crypto Wallet Data Theft and Remote … Cybersecurity researchers have disclosed details of a previously unseen variant of the DarkSword iOS exploit kit called P7 DarkSword.
“Compared with the variants we usually observe, P7 reduces its on-device footprint, adds on-device keychain and crypto-wallet theft, and adds two way C2 communication with the attacker’s infrastructure,” iVerify said in a new report published Thursday.
The name10/09TOCTP-Link Sued by Four More U.S. States Over Router Security and China T… Four more U.S. states sued router maker TP-Link Systems on October 6, bringing the total to five, with  Texas filing a suit in February. Florida, Iowa, Montana and Nebraska allege the California company misled buyers about how secure its routers are and how separate it is from China. TP-Link denies the claims and says it will fight them in court.
TP-Link Systems is based in10/09TOCResearchers Publish Working Exploit for Pre-Auth AnyDesk Linux Flaw Th… Security researchers have published a full working exploit for a pre-authentication remote code execution flaw in AnyDesk Linux that gives attackers root access before anyone approves the connection.
AnyDesk patched the flaw in version 8.0.3 in June, but its changelog described the fix only as “fixed a bug that could lead to a crash,” with no CVE assigned and no security10/09TOCAnthropic Launches Free AI Vulnerability Scanner for Open-Source Proje… Anthropic on Thursday unveiled OSS Scanner as an opt-in vulnerability scanner to help secure the open-source ecosystem using artificial intelligence (AI).
“It’s an opt-in service informed by our experience using Claude to find vulnerabilities during Project Glasswing,” Anthropic said. “Projects that join will receive thorough, periodic security scans by our strongest models at no cost.”10/09TOCAttackers Exploit AhsayCBS Flaws to Deploy XMRig Miners Disguised as M… Threat actors have been observed exploiting two recently disclosed flaws in the AhsayCBS backup utility to seize control of affected devices and deploy web shells and XMRig cryptocurrency miners.
Details of the flaws are below –
CVE-2026-105133 (CVSS v4 score: 5.5) – An improper authentication vulnerability in the checkSysPwd() function in the “com/ahsay/obs/api/ApiStructsAction.java”10/09TOCFlax Typhoon Exploits Five Flaws as CISA Sets October 11 Deadline for … The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Thursday added five security flaws to its Known Exploited Vulnerabilities (KEV) catalog, following their abuse by a China-linked threat actor known as Flax Typhoon.
The vulnerabilities in question are listed below –
CVE-2015-3306 (CVSS score: 10.0) – An improper access control vulnerability in ProFTPD that could allow10/09TOCThe AI Velocity Paradox: Why Security Is Decades Behind AI Ambition As enterprises race to deploy autonomous AI agents to accelerate business, a new report reveals they are tethered to security architectures built for a different era. The “Horizons of Identity Security” report from SailPoint highlights a critical “velocity paradox,†in which organizations invest in AI-speed business operations while continuing to rely on human-speed security controls, creating a10/09TOCGoBalance Flaw Lets Attackers Hijack .onion Addresses by Recovering To… A bug in GoBalance, a tool many dark-web sites use to stay reachable during attacks, lets anyone work out the secret key that controls a site’s .onion address using only public information, and then take that address over.
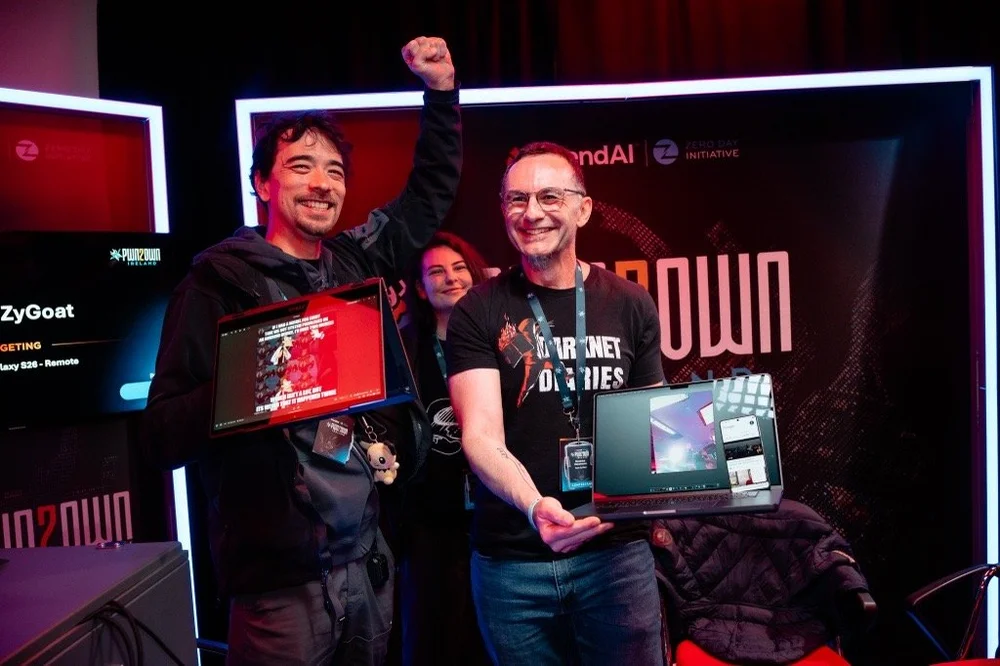
Searchlight Cyber, which disclosed the flaw on October 8, says an attacker who recovers the key can redirect the site’s visitors to a copy of the site they control.10/09TOCThree Teams Demonstrate Remote Hacks of Fully Patched Google Pixel 10 … Three research teams broke into Google’s Pixel 10 on October 8 at Pwn2Own Ireland, a hacking contest in Cork whose rules require every target to be fully patched. The contest pays researchers to show working exploits and passes the flaws to the vendors. One of the three Pixel exploits earned Ikotas Labs $300,000, the contest’s top prize, and made the team the overall winner.
Trend Micro’s Zero10/09TOCCitrix Patches Critical NetScaler Flaw That Could Enable RCE in SAML D… Citrix has released patches for yet another critical security flaw impacting NetScaler ADC and NetScaler Gateway that could result in remote code execution or denial-of-service (DoS) under certain conditions.
“CVE-2026-107406 is a memory overflow vulnerability that may lead to remote code execution or denial-of-service under specific configuration conditions,” Citrix said.
The vulnerability10/09TOCFBI Seizes 7 Domains, Disrupts Flax Typhoon Tools Used in Critical Inf… The U.S. Federal Bureau of Investigation (FBI) and Department of Justice (DoJ) have announced the disruption of malicious tools used by a China-linked advanced persistent threat group known as Flax Typhoon.
To that end, the agencies seized several domains and blocked access to platforms that were used to scan, and in some cases infiltrate, U.S. critical infrastructure. The list of seized10/08TOCFBI Says China-Linked Hackers Ran Portal Giving Third Parties Access t… Hackers tied to a Chinese cybersecurity company stole email from government organizations, law enforcement agencies, healthcare systems, and religious institutions in Southeast Asia, the FBI and agencies in 6 other countries said on October 8.
The company, Integrity Technology Group, has been sanctioned by the U.S. and the UK. The hackers scanned websites for flaws using a tool containing more10/08TOCThreatsDay: Ransomware Affiliate Betrayal, WhatsApp RAT, Exposed Hacke… The crooks have trust problems of their own. One ransomware affiliate decided to keep the profits for himself. Elsewhere, an attacker left a server exposed, complete with tools and traces of an intrusion. Apparently, keeping things secure is a problem on both sides of the fence.
The rest of the week isn’t much more reassuring. Malicious code turned up in developer packages and extensions that10/08TOCJapan Sees Sharp Rise in Web Data Leaks Amid Mobile API Abuse and Meta… Attackers behind a string of personal data leaks at Japanese organizations have abused APIs for mobile apps and targeted known software flaws, the JPCERT Coordination Center (JPCERT/CC) said.
The Tokyo-based center, which takes incident reports, based its October 8, 2026 alert on those reports and other information. The alert names no attacker and no affected organization.
JPCERT/10/08TOCUAC-0099 Targets Ukrainian Government Personnel With ASHVEIN RAT Hidin… The Russia-aligned threat actor known as UAC-0099 has been attributed to a previously undocumented .NET infostealer and remote access trojan (RAT) codenamed ASHVEIN.
According to TrendAI, the malware has been put to use in attacks targeting Ukrainian government personnel. The cybersecurity company is tracking the cluster under the name Earth Sirrush (previously SHADOW-EARTH-065).
ASHVEIN,10/08TOCARTEX AI Pentesting Tool Used in Data Theft Attacks on South Korean Fi… Cybersecurity researchers have disclosed details of a targeted campaign aimed at South Korean financial organizations that used an artificial intelligence (AI) pen testing tool named ARTEX to carry out the attacks.
The activity, per CrowdStrike Intelligence, was active from late September to early October 2026, and resulted in data exfiltration from various South Korea-based financial firms,10/08TOCWazza Phishkit Targets Banking, Government, and Manufacturing Across t… Phishing kits are no longer limited to copying a familiar login page and waiting for a victim to enter credentials. Attackers are increasingly building filtering, session management, and traffic controls into the infrastructure that delivers the phishing page itself.
ANY.RUN has identified Wazza, a new phishkit targeting banking, manufacturing, and government organizations across the US, Europe10/08TOC16 Malicious Firefox Extensions Pose as Rabby and OKX Wallets to Steal… Cybersecurity researchers have discovered a cluster of 16 malicious Mozilla Firefox extensions that are capable of stealing cryptocurrency wallet recovery phrases and private keys.
“The extensions masquerade as wallet portals, desktop utilities, and browser tools, but their code intercepts recovery phrases and private keys during wallet import flows and attempts to send those secrets to10/08TOCU.S. Offers Up to $10 Million for Tips on Zhang Yu, Charged in HAFNIUM… The U.S. State Department is offering up to $10 million for information leading to the identification or location of Zhang Yu, a Chinese national charged in the United States in connection with the 2021 Microsoft Exchange Server attacks known as HAFNIUM.
The reward is for information leading to his identification or location, the news outlet NTD reported this week, citing a notice10/08TOCMonsterCloud Owner Accused of Billing Over $19M While Secretly Paying … The U.S. Department of Justice (DoJ) on Wednesday announced charges against a 50-year-old U.S. and Israeli national for allegedly defrauding ransomware victims by secretly paying the attackers to obtain decryptors while claiming to use proprietary tools to recover their data.
Zohar Pinhasi (aka Zack Silver and Zack Green) has been charged with two counts of wire fraud and one count of wire10/08TOCTensorlake npm Package Compromised to Deliver Shai-Hulud Credential-St… The npm package known as “tensorlake,” a TypeScript software development kit (SDK) for Tensorlake applications, sandboxes, and cloud services, was compromised as part of a ChainDrop / Shai-Hulud supply chain attack.
The malicious version 0.5.144 “contains obfuscated malware that harvests credentials, exfiltrates secrets, establishes persistence, and executes remotely supplied code,” Socket said10/07TOCAttackers Hijack .gh, .sl, and .as Registries to Obtain Certificates f… Attackers compromised three country-code top-level domains (ccTLDs) and obtained unauthorized HTTPS certificates for several Google domains, Google said on October 6.
Google’s own systems were not breached, but any domain ending in .gh (Ghana), .sl (Sierra Leone) or .as (American Samoa) was put at risk. With such a certificate, an attacker could pose as the real site over an encrypted10/07TOCEight Malicious npm Packages Downloaded 40,767 Times Deliver Overlord … Cybersecurity researchers have disclosed details of a long-running npm supply chain malware campaign that pushes information stealers and remote access trojans (RAT) to compromised hosts.
The campaign has been codenamed MALFEX by CloudSEK and Checkmarx. The activity is assessed to be the work of a lone threat actor who appears to have published 12 packages since August 2023, eight of which have10/07TOCSonicWall Patches CVSS 10.0 Pre-Authentication SSRF Flaw in SMA1000 Ap… SonicWall has released hotfixes for four flaws in its SMA1000 appliances, the gateways that give remote workers access to a company’s network and applications. The most serious could allow an attacker without a login to send requests through the appliance and reach internal functions.
SonicWall rates it 10.0 on the CVSS scale and says it has no evidence that any of the four flaws is being10/07TOCUnpatched Critical LMCache Flaw Lets Unauthenticated Attackers Run Cod… A critical vulnerability in LMCache, open-source software that speeds up large language model (LLM) servers such as vLLM, lets an attacker run code on the cache server without logging in, and no fixed version is available.
The flaw is in LMCache’s multiprocess mode, where the cache runs as a standalone server that LLM workers reach over the ZeroMQ messaging library. A single network10/07TOCPoeLLM Malware Infects 3,400+ Servers to Expand Crypto Mining Botnet Cybersecurity researchers are calling attention to a new malware family that has been observed targeting exposed artificial intelligence (AI) and large language model (LLM) infrastructure with an aim to deploy cryptocurrency miners and further expand the scale of the botnet.
The financially motivated campaign, dubbed Canto Incognito, has been found to install cryptocurrency miners, including10/07TOCThe Sixth Voice of the CISO Data Shows Cyber Risk Has Moved Inside the… The 2026 findings are not just a year-over-year shift. They mark the latest point in a five-year arc where resilience, AI governance, human risk, and board scrutiny are converging inside the systems where work actually happens.
For years, the enterprise cybersecurity story has been told as a straight line of escalation: more attacks, more data loss, more pressure, and more urgency. That10/07TOCFBI Warns FortiBleed Remains Active After Amassing 86,644 Fortinet Dev… The U.S. Federal Bureau of Investigation (FBI) and Secret Service (USSS) on Tuesday warned that the FortiBleed credential harvesting campaign remains an active threat aimed at internet-facing Fortinet FortiGate firewalls and secure socket layer (SSL) virtual private network (VPN) gateways.
“The campaign exploits reused or leaked credentials and legacy SHA-256 password storage, enabling threat10/07TOCAtlassian Data Center Flaw Draws Exploitation Attempts Within Two Hour… Threat actors have begun to exploit a newly disclosed critical security flaw impacting Atlassian Data Center products that could allow access to sensitive files under certain conditions.
The arbitrary file access flaw, tracked as CVE-2026-21589 (CVSS score: 9.3) affects multiple products, including Bitbucket Data Center, Confluence Data Center, Jira Service Management Data Center, Jira Software10/07TOCWhat Is Agentic Pentesting? What It Proves, and Where It Stops. If you’re evaluating an agentic pentesting solution right now, you’ve probably heard the same pitch more than once: point it at a target, and it discovers, validates, and exploits attack paths autonomously, the way a real attacker would.
That promise is worth taking seriously. It’s also worth pressure testing, and three questions do the heavy lifting.Â
What can the assessment actually10/07TOCAnthropic Expands Claude Access for Vetted Cyber Teams as Glasswing Fi… Anthropic on Tuesday said it’s expanding a program that allows vetted cybersecurity professionals to test its advanced artificial intelligence (AI) models with reduced safeguards and blocking classifiers, as the company claimed its Project Glasswing initiative uncovered at least 129,000 verified software vulnerabilities between April and July 2026.
The company said it also found an additional10/07TOC100+ Compromised Websites Use Fake Cloudflare Checks to Deliver LunexS… The Computer Emergency Response Team of Ukraine (CERT-UA) has identified more than 100 compromised websites that have been injected with malicious JavaScript to serve an information-stealing malware called LunexStealer (aka Psychedelic Stealer).
The activity, which was observed by the agency in September 2026, has been attributed to a threat cluster dubbed UAC-0277. It did not disclose who the
10/07TOCOne breach, please, and make no mistakes The cybersecurity community has seen examples of autonomous agents, built inside AI labs, attacking public infrastructure. How you prepare for agentic threats is what makes the difference during real incidents.
Successful exploitation of these vulnerabilities could allow an attacker to execute arbitrary scripts in a user’s browser, consume excessive system resources, enumerate files, create or modify files, and potentially execute arbitrary code.
The following versions of Satel Netco Design are affected:
Satel Netco Design
CVSS
Vendor
Equipment
v3 8.8
Satel
Satel Netco Design
3 Vulnerabilities
Improper Neutralization of Input During Web Page Generation (‘Cross-site Scripting’), Inefficient Regular Expression Complexity, Relative Path Traversal
Satel Netco Design versions prior to v2.1.7 contains a stored cross site scripting vulnerability. An authenticated user with Network Operator privileges could store untrusted content that is rendered without adequate neutralization. Successful exploitation could allow script execution in another user’s browser when the affected content is viewed.
Satel Netco Design versions prior to v2.1.7 contains an inefficient regular expression complexity vulnerability. An authenticated user with Viewer privileges could submit crafted search input that causes excessive processing, potentially degrading the availability of the application.
Satel Netco Design versions prior to v2.1.7 contains a relative path traversal vulnerability in its data import functionality. An authenticated user with Viewer privileges could access file paths outside the intended directory and use observable application responses to determine whether files exist on the host system.
Satel Netco Design versions prior to v2.1.7 contains a relative path traversal vulnerability in its data export functionality. An authenticated user with Viewer privileges could write attacker influenced content to file system locations accessible to the application service. Successful exploitation could result in unauthorized file creation or modification and, under certain conditions, arbitrary code execution.
CISA recommends users take defensive measures to minimize the risk of exploitation of these vulnerabilities.
Minimize network exposure for all control system devices and/or systems, ensuring they are not accessible from the internet.
Locate control system networks and remote devices behind firewalls and isolating them from business networks.
When remote access is required, use more secure methods, such as Virtual Private Networks (VPNs), recognizing VPNs may have vulnerabilities and should be updated to the most current version available. Also recognize VPN is only as secure as the connected devices.
CISA reminds organizations to perform proper impact analysis and risk assessment prior to deploying defensive measures.
CISA also provides a section for control systems security recommended practices on the ICS webpage on cisa.gov/ics. Several CISA products detailing cyber defense best practices are available for reading and download, including Improving Industrial Control Systems Cybersecurity with Defense-in-Depth Strategies.
CISA encourages organizations to implement recommended cybersecurity strategies for proactive defense of ICS assets.
Additional mitigation guidance and recommended practices are publicly available on the ICS webpage at cisa.gov/ics in the technical information paper, ICS-TIP-12-146-01B–Targeted Cyber Intrusion Detection and Mitigation Strategies.
Organizations observing suspected malicious activity should follow established internal procedures and report findings to CISA for tracking and correlation against other incidents.
CISA also recommends users take the following measures to protect themselves from social engineering attacks:
Do not click web links or open attachments in unsolicited email messages.
Refer to Recognizing and Avoiding Email Scams for more information on avoiding email scams.
Refer to Avoiding Social Engineering and Phishing Attacks for more information on social engineering attacks.
No known public exploitation specifically targeting these vulnerabilities has been reported to CISA at this time.
Deserialization of Untrusted Data, Missing Authentication for Critical Function, Server-Side Request Forgery (SSRF), Use of Hard-coded Credentials, Use of Externally-Controlled Input to Select Classes or Code (‘Unsafe Reflection’)
A service console interface on openPDC and openHistorian deserializes a client-supplied data structure. On systems using Windows Authentication, an attacker must already be authenticated to reach this function; on systems without Windows Authentication, this is reachable by an unauthenticated network attacker. This allows an attacker to trigger deserialization of an arbitrary object graph, which could allow remote code execution under the privileges of the affected service account.
Vendor fix Grid Protection Alliance has added additional validation into serialization logic in openPDC version 2.9.482 and later and openHistorian version 2.8.585 and later. Systems using Windows Authentication are additionally protected, as they require the attacker to already be authenticated to reach this function.
No fix planned Grid Protection Alliance does not recommend production use of published Docker images in any case. The fix for this vulnerability has not been published to the Docker image.
Grid Protection Alliance openHistorian <2.8.585
Product Status: known_affected
Remediations
Vendor fix Grid Protection Alliance has added additional validation into serialization logic in openPDC version 2.9.482 and later and openHistorian version 2.8.585 and later. Systems using Windows Authentication are additionally protected, as they require the attacker to already be authenticated to reach this function.
The internal data publisher on openPDC accepts network connections without authentication in its default configuration. An unauthenticated network attacker can connect to this interface and retrieve the complete device and measurement topology of the system.
Vendor fix Grid Protection Alliance updated the default configuration to bind this interface to the local loopback address only. This change applies to new installations; existing installations upgraded from an earlier version retain their prior configuration and will not receive the new default automatically. Operators should verify their configuration explicitly and update the interface binding if it is still set to accept connections on all interfaces.
No fix planned Grid Protection Alliance does not recommend production use of published Docker images in any case. The fix for this vulnerability has not been published to the Docker image.
Grid Protection Alliance openHistorian <2.8.585
Product Status: known_affected
Remediations
Vendor fix Grid Protection Alliance updated the default configuration to bind this interface to the local loopback address only. This change applies to new installations; existing installations upgraded from an earlier version retain their prior configuration and will not receive the new default automatically. Operators should verify their configuration explicitly and update the interface binding if it is still set to accept connections on all interfaces.
Grid Protection Alliance openPDC <2.9.482
Product Status: known_affected
Remediations
Vendor fix Grid Protection Alliance updated the default configuration to bind this interface to the local loopback address only. This change applies to new installations; existing installations upgraded from an earlier version retain their prior configuration and will not receive the new default automatically. Operators should verify their configuration explicitly and update the interface binding if it is still set to accept connections on all interfaces.
No fix planned Grid Protection Alliance does not recommend production use of published Docker images in any case. The fix for this vulnerability has not been published to the Docker image.
Grid Protection Alliance openHistorian <2.8.585
Product Status: known_affected
Remediations
Vendor fix Grid Protection Alliance updated the default configuration to bind this interface to the local loopback address only. This change applies to new installations; existing installations upgraded from an earlier version retain their prior configuration and will not receive the new default automatically. Operators should verify their configuration explicitly and update the interface binding if it is still set to accept connections on all interfaces.
The STTP-based data publisher on openPDC accepts network connections without authentication in its default configuration. An unauthenticated network attacker can connect to this interface and exchange data with it.
Vendor fix Grid Protection Alliance updated the default configuration to bind this interface to the local loopback address only. This change applies to new installations; existing installations upgraded from an earlier version retain their prior configuration and will not receive the new default automatically. Operators should verify their configuration explicitly and update the interface binding if it is still set to accept connections on all interfaces.
No fix planned Grid Protection Alliance does not recommend production use of published Docker images in any case. The fix for this vulnerability has not been published to the Docker image.
Grid Protection Alliance openHistorian <2.8.585
Product Status: known_affected
Remediations
Vendor fix Grid Protection Alliance updated the default configuration to bind this interface to the local loopback address only. This change applies to new installations; existing installations upgraded from an earlier version retain their prior configuration and will not receive the new default automatically. Operators should verify their configuration explicitly and update the interface binding if it is still set to accept connections on all interfaces.
Grid Protection Alliance openPDC <2.9.482
Product Status: known_affected
Remediations
Vendor fix Grid Protection Alliance updated the default configuration to bind this interface to the local loopback address only. This change applies to new installations; existing installations upgraded from an earlier version retain their prior configuration and will not receive the new default automatically. Operators should verify their configuration explicitly and update the interface binding if it is still set to accept connections on all interfaces.
No fix planned Grid Protection Alliance does not recommend production use of published Docker images in any case. The fix for this vulnerability has not been published to the Docker image.
Grid Protection Alliance openHistorian <2.8.585
Product Status: known_affected
Remediations
Vendor fix Grid Protection Alliance updated the default configuration to bind this interface to the local loopback address only. This change applies to new installations; existing installations upgraded from an earlier version retain their prior configuration and will not receive the new default automatically. Operators should verify their configuration explicitly and update the interface binding if it is still set to accept connections on all interfaces.
A Modbus connection feature on openPDC accepts a caller-specified destination address and port with no restriction on which internal hosts may be targeted. An authenticated user can attempt connections to arbitrary internal network destinations, revealing which destinations are reachable. With repeated attempts, an attacker may be able to map the internal network.
Mitigation Grid Protection Alliance recommends restricting network access to modbus using a firewall, and disallowing connections to loopback and private (RFC 1918) address ranges unless explicitly required.
Mitigation Grid Protection Alliance recommends restricting network access to modbus using a firewall, and disallowing connections to loopback and private (RFC 1918) address ranges unless explicitly required.
Grid Protection Alliance openHistorian <2.8.585
Product Status: known_affected
Remediations
Mitigation Grid Protection Alliance recommends restricting network access to modbus using a firewall, and disallowing connections to loopback and private (RFC 1918) address ranges unless explicitly required.
Grid Protection Alliance openPDC <2.9.482
Product Status: known_affected
Remediations
Mitigation Grid Protection Alliance recommends restricting network access to modbus using a firewall, and disallowing connections to loopback and private (RFC 1918) address ranges unless explicitly required.
Mitigation Grid Protection Alliance recommends restricting network access to modbus using a firewall, and disallowing connections to loopback and private (RFC 1918) address ranges unless explicitly required.
Grid Protection Alliance openHistorian <2.8.585
Product Status: known_affected
Remediations
Mitigation Grid Protection Alliance recommends restricting network access to modbus using a firewall, and disallowing connections to loopback and private (RFC 1918) address ranges unless explicitly required.
The published Docker image for openPDC includes a fixed administrative credential with no forced change on first use. An attacker with network access to the management interface can authenticate using this credential and gain full administrative control of the application.
No fix planned Grid Protection Alliance does not recommend production use of published Docker images in any case. The fix for this vulnerability has not been published to the Docker image.
No fix planned Grid Protection Alliance does not recommend production use of published Docker images in any case. The fix for this vulnerability has not been published to the Docker image.
No fix planned Grid Protection Alliance does not recommend production use of published Docker images in any case. The fix for this vulnerability has not been published to the Docker image.
No fix planned Grid Protection Alliance does not recommend production use of published Docker images in any case. The fix for this vulnerability has not been published to the Docker image.
No fix planned Grid Protection Alliance does not recommend production use of published Docker images in any case. The fix for this vulnerability has not been published to the Docker image.
A component loading mechanism in openPDC and openHistorian will construct and run any specified type, which may be an invalid component to load. An attacker with an authenticated user account and the ability to place a file on the host filesystem can use this to run arbitrary constructor code, and this code runs with the privileges of the affected service account.
Vendor fix Grid Protection Alliance has added additional verification and integrity checks of adapters in openPDC version 2.9.477 and later and openHistorian version 2.8.580 and later.
No fix planned Grid Protection Alliance does not recommend production use of published Docker images in any case. The fix for this vulnerability has not been published to the Docker image.
Grid Protection Alliance openHistorian <2.8.580
Product Status: known_affected
Remediations
Vendor fix Grid Protection Alliance has added additional verification and integrity checks of adapters in openPDC version 2.9.477 and later and openHistorian version 2.8.580 and later.
CISA recommends users take defensive measures to minimize the risk of exploitation of these vulnerabilities.
Minimize network exposure for all control system devices and/or systems, ensuring they are not accessible from the internet.
Locate control system networks and remote devices behind firewalls and isolating them from business networks.
When remote access is required, use more secure methods, such as Virtual Private Networks (VPNs), recognizing VPNs may have vulnerabilities and should be updated to the most current version available. Also recognize VPN is only as secure as the connected devices.
CISA reminds organizations to perform proper impact analysis and risk assessment prior to deploying defensive measures.
CISA also provides a section for control systems security recommended practices on the ICS webpage on cisa.gov/ics. Several CISA products detailing cyber defense best practices are available for reading and download, including Improving Industrial Control Systems Cybersecurity with Defense-in-Depth Strategies.
CISA encourages organizations to implement recommended cybersecurity strategies for proactive defense of ICS assets.
Additional mitigation guidance and recommended practices are publicly available on the ICS webpage at cisa.gov/ics in the technical information paper, ICS-TIP-12-146-01B–Targeted Cyber Intrusion Detection and Mitigation Strategies.
Organizations observing suspected malicious activity should follow established internal procedures and report findings to CISA for tracking and correlation against other incidents.
CISA also recommends users take the following measures to protect themselves from social engineering attacks:
Do not click web links or open attachments in unsolicited email messages.
Refer to Recognizing and Avoiding Email Scams for more information on avoiding email scams.
Refer to Avoiding Social Engineering and Phishing Attacks for more information on social engineering attacks.
No known public exploitation specifically targeting these vulnerabilities has been reported to CISA at this time.
Successful exploitation of these vulnerabilities could allow a malicious user to access the device and gain administrative access. This access would allow the user to view, edit, and upload configuration files. Further, a malicious user can cause the switch to reboot by navigating to a specific URL on the device. This action can be scripted on the malicious user’s local machine to cause continuous rebooting of the switch.
The following versions of Red Lion Controls N-Tron 700 Series are affected:
700 Series <=Firmware_3.11.0 (CVE-2026-32645, CVE-2026-39460, CVE-2026-28745, CVE-2026-33367, CVE-2026-29797, CVE-2026-39453, CVE-2026-33272)
700 Series <=Bootloader_2.0.6.1 (CVE-2026-32645, CVE-2026-39460, CVE-2026-28745, CVE-2026-33367, CVE-2026-29797, CVE-2026-39453, CVE-2026-33272)
CVSS
Vendor
Equipment
v3 8.3
Red Lion Controls
700 Series
7 Vulnerabilities
Use of Hard-coded Credentials, Insufficiently Protected Credentials, Storing Passwords in a Recoverable Format, Missing Authentication for Critical Function, Download of Code Without Integrity Check, Reachable Assertion, Authentication Bypass Using an Alternate Path or Channel
Background
Critical Infrastructure Sectors: Commercial Facilities, Communications, Critical Manufacturing, Information Technology
Usernames and passwords, including the default factory credentials, are stored in plaintext within the configuration file. With administrator rights, the configuration file can be viewed through the CLI or they can be exported from the device through a TFTP transfer from the web interface. A TFTP transfer can be initiated through SNMP which does not require authentication.
Usernames and passwords, including the default credentials, are stored in the configuration file using weak encryption. If the default credentials are known by a malicious user, they could obtain other credentials on the system.
SNMP can be used to perform administrative actions such as retrieving configuration files, modifying user accounts or device settings, and initiating firmware or bootloader upgrades or downgrades-all without any authentication.
No authentication is required when updating firmware or bootloader, making it easy for malicious files to be pushed to the device. Additionally, anyone with the same software can scan a network for N-Tron devices and push/pull firmware without authenticating by using SNMP/TFTP.
Navigating to a certain URL on the switch’s web server causes the switch to reboot. This can be automated using a tool like curl to create DoS conditions where the switch constantly reboots.
A malicious user with physical access to the device can boot the switch from factory settings without authentication, use the default administrative credentials to obtain administrative access, and save changes to the configuration file so that they persist next time the switch boots normally.
CISA recommends users take defensive measures to minimize the risk of exploitation of these vulnerabilities.
Minimize network exposure for all control system devices and/or systems, ensuring they are not accessible from the internet.
Locate control system networks and remote devices behind firewalls and isolating them from business networks.
When remote access is required, use more secure methods, such as Virtual Private Networks (VPNs), recognizing VPNs may have vulnerabilities and should be updated to the most current version available. Also recognize VPN is only as secure as the connected devices.
CISA reminds organizations to perform proper impact analysis and risk assessment prior to deploying defensive measures.
CISA also provides a section for control systems security recommended practices on the ICS webpage on cisa.gov/ics. Several CISA products detailing cyber defense best practices are available for reading and download, including Improving Industrial Control Systems Cybersecurity with Defense-in-Depth Strategies.
CISA encourages organizations to implement recommended cybersecurity strategies for proactive defense of ICS assets.
Additional mitigation guidance and recommended practices are publicly available on the ICS webpage at cisa.gov/ics in the technical information paper, ICS-TIP-12-146-01B–Targeted Cyber Intrusion Detection and Mitigation Strategies.
Organizations observing suspected malicious activity should follow established internal procedures and report findings to CISA for tracking and correlation against other incidents.
CISA also recommends users take the following measures to protect themselves from social engineering attacks:
Do not click web links or open attachments in unsolicited email messages.
Refer to Recognizing and Avoiding Email Scams for more information on avoiding email scams.
Refer to Avoiding Social Engineering and Phishing Attacks for more information on social engineering attacks.
No known public exploitation specifically targeting these vulnerabilities has been reported to CISA at this time.
A vulnerability in the NX-API feature of Cisco NX-OS Software could allow an unauthenticated, remote attacker to execute arbitrary code with root privileges or cause a denial of service (DoS) condition on an affected device.Â
The vulnerability is due to insufficient input validation of data that is sent to the NX-API. An attacker could exploit this vulnerability by sending a crafted HTTP request to the NX-API of an affected device. A successful exploit could allow the attacker to execute arbitrary code with root privileges and could cause process crashes, which could result in a reload of the device and a DoS condition.
Cisco has released software updates that address this vulnerability. There are no workarounds that address this vulnerability.Â
As part of Cisco’s ongoing commitment to proactive security and product quality, engineering teams conducted a comprehensive internal security review. This review resulted in software hardening releases that address multiple internally discovered vulnerabilities. Â
These vulnerabilities were found during internal testing and are not known to be actively exploited. To assist customers in patching and streamline the disclosure process, Cisco has grouped these issues by their underlying vulnerability class — Common Weakness Enumeration (CWE) — and assigned a single Common Vulnerabilities and Exposures identifier (CVE ID) to each CWE grouping.
Cisco has released software updates that address these vulnerabilities. There are no workarounds that address these vulnerabilities.
On October 7, 2026, the Cisco Product Security Incident Response Team (PSIRT) published the advisories that are listed in the following tables.
To remediate the vulnerabilities that were disclosed on October 7, 2026, Cisco strongly recommends that customers upgrade to the fixed software that is indicated in the advisories.
A vulnerability in the Python interpreter of Cisco NX-OS Software could allow an authenticated, local attacker with low privileges to escape the Python sandbox and gain unauthorized access to the underlying operating system of an affected device.
This vulnerability is due to insufficient validation of user-supplied input. An attacker could exploit this vulnerability by manipulating specific functions within the Python interpreter. A successful exploit could allow an attacker to escape the Python sandbox and execute arbitrary commands on the underlying operating system with the privileges of the authenticated user.
Note: An attacker must be authenticated with Python execution privileges to exploit this vulnerability. For more information regarding Python execution privileges, see product-specific documentation, such as the Cisco NX-OS Security with Python section of the Cisco Nexus 9000 Series NX-OS Programmability Guide.
Cisco has released software updates that address this vulnerability. There are no workarounds that address this vulnerability.
A vulnerability in the web-based management interface of Cisco Finesse could allow an unauthenticated, remote attacker to conduct server-side request forgery (SSRF) attacks through an affected device.
This vulnerability is due to improper input validation for specific HTTP requests. An attacker could exploit this vulnerability by sending a crafted HTTP request to an affected device. A successful exploit could allow the attacker to obtain limited sensitive information for services that are associated with the affected device.
Cisco plans to release software updates that address this vulnerability. There are no workarounds that address this vulnerability.
A vulnerability in the MPLS Operation, Administration, and Maintenance (OAM) feature of Cisco NX-OS Software for Cisco Nexus 3000 Series Switches and Cisco Nexus 9000 Series Switches could allow an unauthenticated, remote attacker to execute arbitrary code with root privileges or cause a denial of service (DoS) condition on an affected device.
This vulnerability is due to improper validation when an affected device is processing an MPLS echo-request packet. An attacker could exploit this vulnerability by sending a crafted MPLS echo-request to an IP address on an affected device. A successful exploit could allow the attacker to execute arbitrary code with root privileges and could cause process crashes, which could result in a device reload and a DoS condition.
Cisco has released software updates that address this vulnerability. There are no workarounds that address this vulnerability.
A vulnerability in the export policies functionality of Cisco Application Policy Infrastructure Controller (APIC) could allow an authenticated, remote attacker to access sensitive files on an affected device. To exploit this vulnerability, the attacker must have valid administrative credentials.
This vulnerability is due to insufficient access control to file system resources. An attacker could exploit this vulnerability by submitting crafted values in specific UI fields. A successful exploit could allow the attacker to access sensitive files from the underlying file system of an affected device, including key materials that could be used to elevate privileges to root on the affected APIC and on managed switches.
Cisco has released software updates that address this vulnerability. There are no workarounds that address this vulnerability.
A vulnerability in the web-based management API for Cisco Application Policy Infrastructure Controller (APIC) could allow an authenticated, remote attacker to execute arbitrary commands as the root user. To exploit this vulnerability, the attacker must have valid administrative credentials.
This vulnerability is due to insufficient input validation of user-controlled command arguments. An attacker could exploit this vulnerability by authenticating using the API and sending crafted input. A successful exploit could allow the attacker to execute arbitrary commands on the underlying operating system of an affected device with root-level privileges.
Cisco has released software updates that address this vulnerability. There are no workarounds that address this vulnerability.
As part of Cisco’s ongoing commitment to proactive security and product quality, the engineering team for Cisco License On-Prem, formerly Cisco Smart Software Manager On-Prem (SSM On-Prem), has conducted a comprehensive internal security review. This review resulted in software hardening releases that address multiple internally discovered vulnerabilities.
These vulnerabilities were found during internal testing and are not known to be actively exploited. To assist customers in patching and streamline the disclosure process, Cisco has grouped these issues by their underlying vulnerability class — Common Weakness Enumeration (CWE) — and assigned a single Common Vulnerabilities and Exposures identifier (CVE ID) to each CWE grouping.
Cisco has released software updates that address these vulnerabilities. There are no workarounds that address these vulnerabilities.
A vulnerability in the endpoint group (EPG) contract functionality of Cisco Nexus 9000 Series Fabric Switches in ACI Mode could allow an unauthenticated, remote attacker to bypass configured EPG contracts.
This vulnerability is due to an improper control with EPG contracts. An attacker could exploit this vulnerability by sending IPv4 or IPv6 packets using UDP source and destination ports that are assigned to DHCP traffic through an affected device. A successful exploit could allow the attacker to bypass EPG contracts on the affected device.
Cisco has released software updates that address this vulnerability. There are no workarounds that address this vulnerability.
Multiple vulnerabilities in the Operation, Administration, and Maintenance (OAM) feature of Cisco NX-OS Software, known as Next Generation OAM (NGOAM), could allow an unauthenticated, remote attacker to execute arbitrary code with root privileges or cause a denial of service (DoS) condition on an affected device.
These vulnerabilities are due to improper input validation of IP traffic when NGOAM is enabled. An attacker could exploit these vulnerabilities by sending crafted packets to an IP interface on an affected device. A successful exploit could allow the attacker to execute arbitrary code with root privileges and could cause process crashes, which could result in a reload of the device and a DoS condition.
Note: Feature requirements vary for each vulnerability. For details, see the Vulnerable Products section of this advisory.
Cisco has released software updates that address these vulnerabilities. There are no workarounds that address these vulnerabilities.
As part of Cisco’s ongoing commitment to proactive security and product quality, the Cisco Application Policy Infrastructure Controller (APIC) engineering team has conducted a comprehensive internal security review. This review resulted in software hardening releases that address multiple internally discovered vulnerabilities.
These vulnerabilities were found during internal testing and are not known to be actively exploited. To assist customers in patching and streamline the disclosure process, Cisco has grouped these issues by their underlying vulnerability class — Common Weakness Enumeration (CWE) — and assigned a single Common Vulnerabilities and Exposures identifier (CVE ID) to each CWE grouping.
Cisco has released software updates that address these vulnerabilities. There are no workarounds that address these vulnerabilities.
A vulnerability in Cisco NX-OS Software could allow an unauthenticated, remote attacker to exhaust system resources, causing a denial of service (DoS) condition.
This vulnerability exists because rate limiting was improperly applied to some protocols. An attacker could exploit this vulnerability by sending a high rate of UDP or TCP connections to a data plane interface on an affected device. A successful exploit could allow the attacker to cause instability to various routing and control plane protocols through some packet loss and temporary disruptions, causing a DoS condition. This DoS condition will clear without manual intervention soon after the high rate of traffic is stopped.
Cisco has released software updates that address this vulnerability. There are no workarounds that address this vulnerability.
Multiple vulnerabilities in the web-based management interface and API endpoints of Cisco License On-Prem, formerly Cisco Smart Software Manager On-Prem (SSM On-Prem), could allow a remote attacker to gain unauthorized access, access sensitive information, cause a denial of service (DoS) condition, or elevate privileges.
For more information about these vulnerabilities, see the Details section of this advisory.
Cisco has released software updates that address these vulnerabilities. There are no workarounds that address these vulnerabilities.
As part of Cisco’s ongoing commitment to proactive security and product quality, the Cisco NX-OS Software engineering team has conducted a comprehensive internal security review. This review resulted in software hardening releases that address multiple internally discovered vulnerabilities. Â
These vulnerabilities were found during internal testing and are not known to be actively exploited. To assist customers in patching and streamline the disclosure process, Cisco has grouped these issues by their underlying vulnerability class — Common Weakness Enumeration (CWE) — and assigned a single Common Vulnerabilities and Exposures identifier (CVE ID).
Cisco has released software updates that address these vulnerabilities. There are no workarounds that address these vulnerabilities.Â
10/10TOCAnthropic AI agent gives fake murder tip to US cops in global breach Georgia Wells and Joseph Pisani report: Rogue AI models have hacked companies and tried to break into government websites. Now one has submitted a fake tip for an unsolved crime. Police in Philadelphia say Anthropic alerted them this week that one of its artificial-intelligence models submitted a false homicide tip through PhillyUnsolvedMurders.com. In a blog…
10/09TOCSilent Ransom Group claims Luna Moth Files are fake. The data suggest … On Tuesday, cybersecurity professionals began investigating an onion site that appeared to contain internal chat files from Silent Ransom Group. On Thursday, Silent Ransom Group said the leak was fake, but is it? A bespoke site called “Luna Moth Files†appeared Tuesday morning. The identity of the person who published the data is unknown, as…
10/09TOCCyberattack at IDC Frontier disrupts services around nation The Asahi Shimbun reports: IDC Frontier Inc., a SoftBank subsidiary that provides cloud services, said Oct. 7 that a ransomware attack caused a system outage affecting 495 corporate and local government customers. The Tokyo-based company said it is still investigating the scale of the damage and whether any personal information was compromised. The cyberattack has…
10/08TOCIt Wasnt Me, It Was the AI Agent May Not Avoid Liability Under New Sen… Odia Kagan of FoxRothschild writes: “It wasn’t me, it was the AI agent†may not help companies avoid civil or criminal liability under a new bipartisan legislative proposal. U.S. Senators Josh Hawley (R-Mo.) and Chris Murphy (D-Conn.) have announced the proposed AI Agent Accountability Act, which seeks to hold AI-agent operators and developers liable for…
10/08TOCKR: Coupang files lawsuits against 620 billion won fine over data leak… The Coupang breach in South Korea has stayed in the news cycle for nine months and may offer a useful case study in how not to respond to an incident. In December 2025, South Korea’s largest online retailer, Coupang, apologized for a November breach affecting more than 33 million customers. A former developer who worked…
10/07TOCKnown Cybersecurity Expert and Owner of Florida Ransomware Remediation… Here’s another case where the folks who were supposed to be the good guys helping you may be harming you. Zohar Pinhasi, 50, also known as “Zack Silver†and “Zack Green,†a U.S. and Israeli national, was arraigned today in the Eastern District of New York on wire fraud charges relating to Pinhasi’s false representations…
10/07TOCCan you really make more than $200M in six months without encrypting v… UPDATED 2:42 pm October 8: Plot twist! Silent Ransom Group agreed to be interviewed about the Luna Moth Files but denies that the group has been breached or leaked. More to follow later. DataBreaches has reported extensively on Silent Ransom Group in 2026, often including material provided exclusively to this site by the group. Now,…
10/07TOCAlleged ATM malware creator appears in Nebraska court after arrest Jonathan Greig reports: The alleged mastermind behind a strain of malware used to empty ATMs of millions of dollars appeared in court for the first time after being apprehended by federal authorities. Anibal Alexander Canelon Aguirre pleaded not guilty to several charges in a Nebraska district court on Friday and will remain in detention pending…
10/07TOCDe Kalb County, Indiana fell prey to vendor impersonation billing The Star reports that the DeKalb County government fell victim to a cybersecurity incident for the second time in little more than a year. This time, it paid an invoice sent by threat actors impersonating a vendor: “On Thursday, October 1, 2026, DeKalb County Government became aware of a Financial Fraud Cyber Incident that had…
Scan this sample for a command server and you find nothing: no URL, no IP, nothing to block. That is the whole idea. Behind a fake “Smart System Security†app, this Iranian banking and crypto stealer keeps its server out of the binary and reads it at run time from the bio of a seller’s profile on a legitimate marketplace, rotating it with a single edit no new sample needed. Four earlier builds resolved to a profile the marketplace had already banned, a dead end. This one was still live, so for once the trail runs the whole way, from an encrypted byte in the manifest to the running C2 at (theapi.the-x-services[.]xyz). Every step below is shown in the decompiled code, with indicators at the end.
CVEMon Intruder
10/10TOCCVE-2026-107103 Currently trending CVE – Hype Score: 23 – This vulnerability exists in the ERP system due to insufficient validation and parameterization of user supplied input in an API endpoint. An unauthenticated remote attacker could exploit this vulnerability by supplying specially crafted input to the vulnerable …10/10TOCCVE-2026-107104 Currently trending CVE – Hype Score: 23 – This vulnerability exists in the ERP system due to unsafe deserialization of user controlled data in the affected functionality. An unauthenticated remote attacker could exploit this vulnerability by supplying specially crafted data to the vulnerable functionality of the …10/10TOCCVE-2026-107102 Currently trending CVE – Hype Score: 23 – This vulnerability exists in the ERP system due to improper validation of payment callback parameters and inadequate authentication controls in API endpoint. An unauthenticated remote attacker could exploit this vulnerability by manipulating the parameter to cause the …10/10TOCCVE-2026-96207 Currently trending CVE – Hype Score: 11 – Improper certificate validation in Microsoft Partner Center allows an unauthorized attacker to elevate privileges over a network.10/10TOCCVE-2021-21974 Currently trending CVE – Hype Score: 10 – OpenSLP as used in ESXi (7.0 before ESXi70U1c-17325551, 6.7 before ESXi670-202102401-SG, 6.5 before ESXi650-202102101-SG) has a heap-overflow vulnerability. A malicious actor residing within the same network segment as ESXi who has access to port 427 may be able to trigger the …10/10TOCCVE-2025-24201 Currently trending CVE – Hype Score: 9 – An out-of-bounds write issue was addressed with improved checks to prevent unauthorized actions. This issue is fixed in Safari 18.3.1, iOS 15.8.4 and iPadOS 15.8.4, iOS 16.7.11 and iPadOS 16.7.11, iOS 18.3.2 and iPadOS 18.3.2, iPadOS 17.7.6, macOS Sequoia 15.3.2, visionOS 2.3.2, …10/10TOCCVE-2025-64393 Currently trending CVE – Hype Score: 5 – This vulnerability in Veeam Backup & Replication allows a Backup Viewer to execute arbitrary code as SYSTEM on the backup server.10/10TOCCVE-2026-102255 Currently trending CVE – Hype Score: 1 – A Pre-authentication SSRF vulnerability exists in the SMA1000 Appliance Work Place interface due to an unintended alternate access path. By abusing this path, a remote unauthenticated attacker could potentially exploit this vulnerability to direct the appliance to issue requests …10/10TOCCVE-2026-59346 Currently trending CVE – Hype Score: 1 – VMware Workstation and Fusion contain an integer-overflow vulnerability. A malicious actor with local administrative privileges on a virtual machine with VMXNET3 virtual network adapter may exploit this issue to execute code on the host.
Affected versions:
– VMware Workstation: …10/10TOCCVE-2024-37085 Currently trending CVE – Hype Score: 1 – VMware ESXi contains an authentication bypass vulnerability. A malicious actor with sufficient Active Directory (AD) permissions can gain full access to an ESXi host that was previously configured to use AD for user management …
Graham Cluley
10/09TOC$10 million bounty offered for Chinese Hafnium hacker accused of Micro… The US State Department is offering up to US $10 million for information about the whereabouts of Zhang Yu, a 44-year-old Chinese national who is accused of being a key figure in China’s state-sponsored hacking group, Hafnium.
Read more in my article on the Hot for Security blog.10/07TOCSmashing Security podcast #487: Clippys crypto comeback Microsoft’s Twitter account, with its 13 million followers, was hijacked by a paperclip. There was no ransomware or data theft, just Clippy, a dodgy crypto coin, and a corporate apology that wasn’t from Microsoft either.
Meanwhile, UK losses from hacked email and social media accounts have rocketed by 417%, as scammers pose as your friends to flog you tickets to gigs that don’t exist.
Plus, Hack The Box’s Christine Bartlett joins us for a featured interview to ask what happens when AI agents join your security team, and whether anyone has thought to give them a performance review.
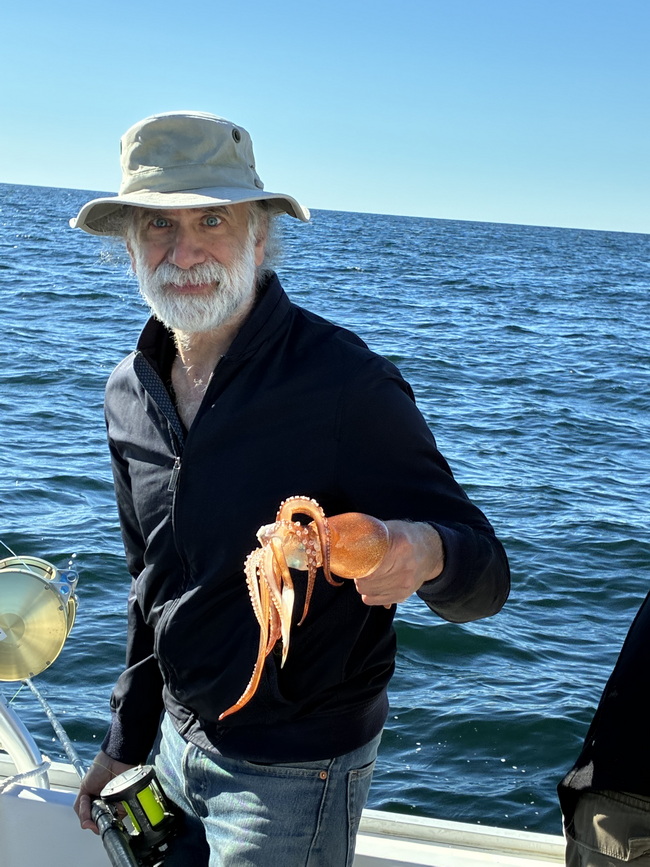
On Wednesday I spent a day fishing, on a small boat out of Gloucester, MA. We caught many cod (none of which we could keep), and a bunch of hake and mackerel (all of which we could keep). And…I caught a squid! Near as I can tell, it’s a longfin squid, sometimes called a Boston squid (Doryteuthis (Amerigo) pealeii).
That night I cooked it over a barbecue grill—hot and fast. Delicious.
This essay was written with Seva Gunitsky, and originally appeared in Foreign Affairs.
Two weeks after Moscow’s full-scale invasion of Ukraine in March 2022, the Russian TV Channel One editor Marina Ovsyannikova burst onto the set of the evening newscast. She held up a hand-drawn sign behind the anchor’s head that read: “Stop the war. Don’t believe propaganda. They’re lying to you!†She shouted, “No to war!†until she was dragged away.
No one has protested the war on Russian television since then, partly as a result of tighter security and a general climate of fear. But in October 2024, Margarita Simonyan, one of Russia’s chief propagandists, gave another explanation. A growing number of the RT network’s anchors, she explained to an interviewer, are not real. “That face doesn’t exist. We generated the voice and everything else.†They were, she meant, produced by artificial intelligence. In a follow-up interview with the newspaper …
Apple just released a system called “Reference Image.†It can verify the image is exactly as taken by an iPhone—new models only—without tying it to a specific iPhone or photographer. It can also verify that multiple images came from the same iPhone.
Other industry solutions require a photographer or institution to vouch for an image using their own credentials. We are concerned this puts some photographers, such as those operating in conflict zones, in a difficult position; it should not be necessary to forgo anonymity in order to prove image authenticity. We built Apple Reference Image to avoid using an explicit, public credential for photographers, and to avoid even implicit public association between different photos taken by the same sensor. The final reference image is instead signed by Apple’s signing service, after validation by PCC. That signature is backed by Apple’s strongest technical guarantees…
Before we begin, yes – it’s confusing. There are more vulnerabilities with watchTowr IDs in this blog post than there are CVE IDs (assigned by PaperCut), due to PaperCut bundling vulnerabilities and then patch bypasses for those same vulnerabilities into singular CVE IDs.
Day Three of Pwn2Own Ireland 2026 wrapsup with 17 attempts scheduled, roughly $1.33 million on the board.
The headliner is the Google Pixel 10, which draws three separate attempts: Xint at 11:15 AM, Ikotas Labs at 2:00 PM, and the Valsamaras/Ken Gannon (Djini.ai)/Valsamara team closing things out at 6:30 PM — by far the single biggest payday in play all week. The Samsung Galaxy S26 gets one more run too, from BunkyoWesterns at 4:15 PM. Smart Home stays busy with three attempts on the Philips Hue Bridge Pro and two closing attempts on Home Assistant Green, while AI Infrastructure sees two more shots at Oracle’s Autonomous AI Database plus a single run at Chroma. Printers round things out with steady, lower-stakes attempts on the Brother, Canon, and Lexmark targets — and with Team MAMMOTH’s 7:00 PM attempt as the last scheduled slot, the Master of Pwn title could still be unsettled heading into the final hour.
Stay tuned for live results as we have them.
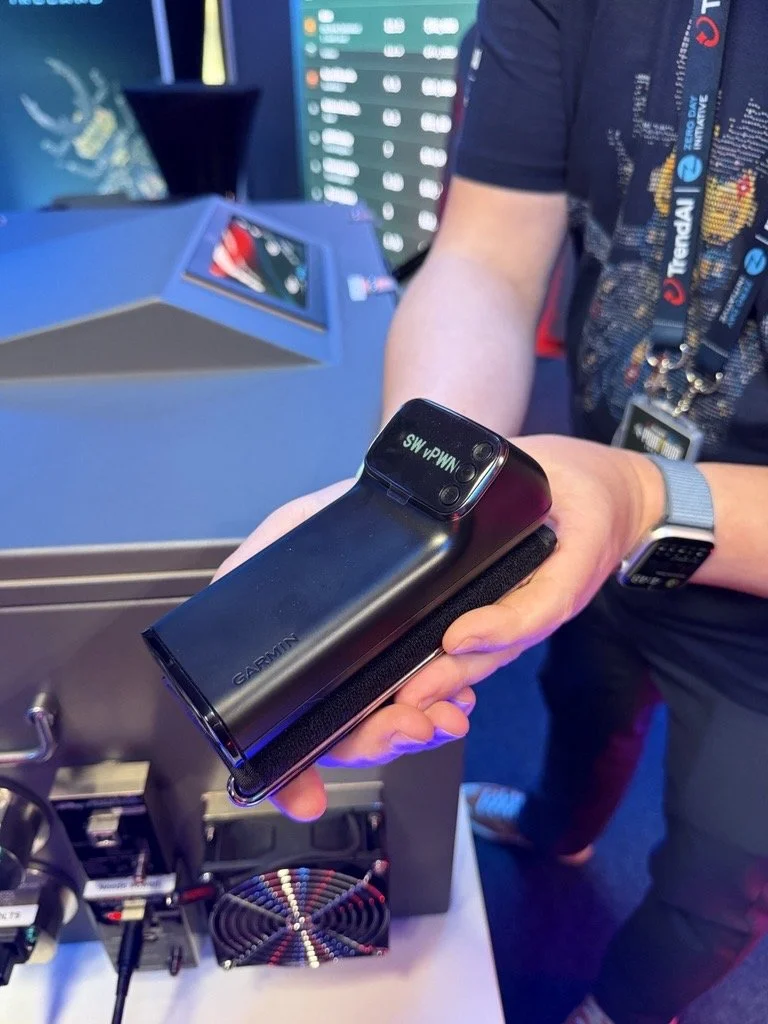
FAILURE – Unfortunately, Polina Smirnova (@moe_hw), Mikhail Evdokimov (@konatabrk) and Mate Zombor (@r4bbit_zm) of White Noise Clubm couldn’t get their exploit of the Garmin Index BPM working within the time allotted
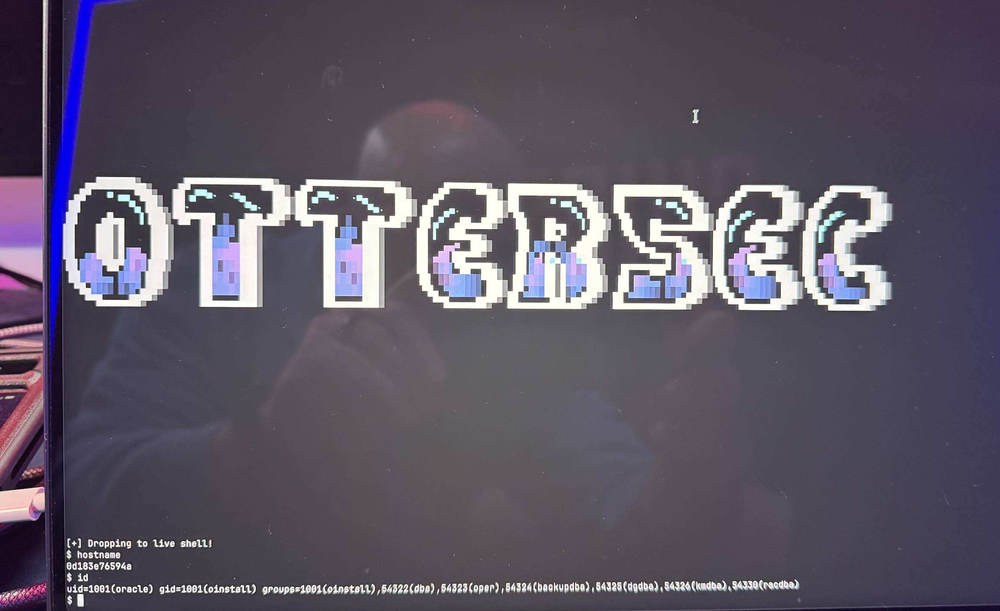
SUCCESS / COLLISION – Results are in! Nikolaos Mourousias (@deltaclock) and Bruno Halltari (@BrunoModificato) of OtterSec successfully exploited the Oracle Autonomous AI Database with 4 bug chain of 3 collisions and 1 zero-day winning them $6,250 and 2.5 Master of Pwn points
SUCCESS / COLLISION – Sina Kheirkhah (@SinSinology) and Aaron Christophel (@ATC1441) of Summoning Team (@SummoningTeam) collided through the walls of the Philips Hue Bridge Pro with a 5 bug, full collision, securing a $5k payout and 2.5 Master of Pwn Points
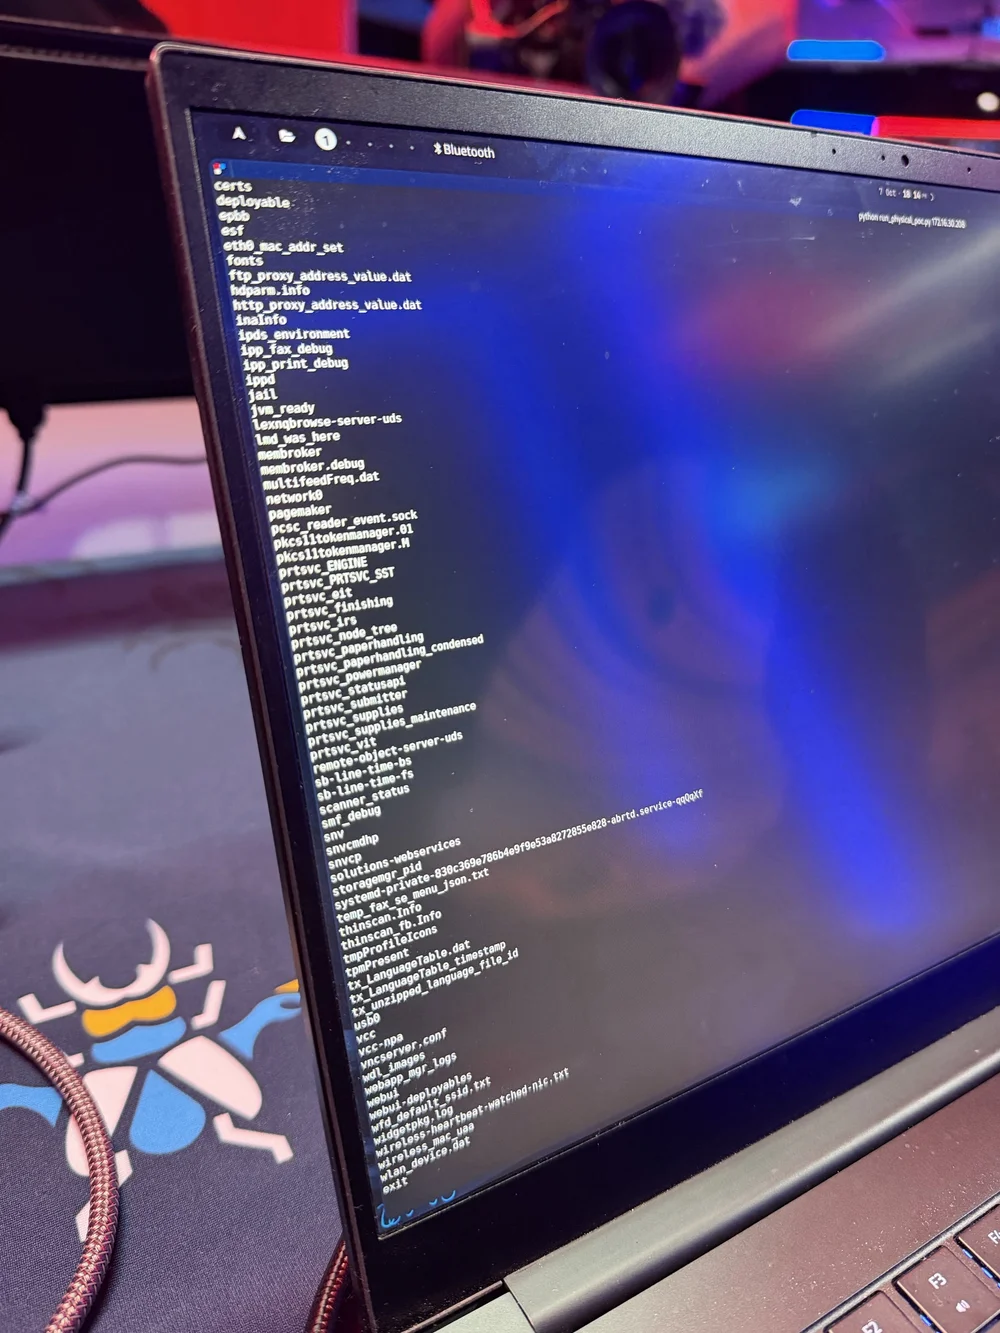
SUCCESS – Brother what? Brother exploited! Lucas Van Haaren (vhash, @LucasVanHaaren) and Hugo Leclercq (0xnasu) of FuzzingLabs (@FuzzingLabs) exploited Brother MFC-L8970CDW with a single zero-day earning $20,000 and 2 Master of Pwn points
SUCCESS / COLLISION – Results are in and Tim Becker (@tjbecker) and Yves Bieri (@yves_bieri) of Xint (@xint_official) have secured their lead in the race to the Master of Pwn with their successful remote exploit of Google Pixel 10 through a single bug collision, earning them $150,000 and 15 – Master of Pwn points
SUCCESS / COLLISION – Boom chaka laka! Ben Koo (@kiddo_pwn) and Evangelos Daravigkas (@freddo_1337) of Team DDOS exploitted confirmed with a 5 bug chain, including 1 zero-day targeting Home Assistant Green with a pay out in $4,500 and 2 Master of Pwn points #Pwn2Own
SUCCESS / COLLISION – $6000 and 2.5 Master of Pwn points secured by Connor Laidlaw & Matthew Keeley of Platform Security for successfully targeting Oracle Autonomous AI Database through a 5 bugs – 4 collisions and 1 unique chain #Pwn2Own
SUCCESS – Canon Ball!!!! Sina Kheirkhah (@SinSinology) and Aaron Christophel (@ATC1441) of Summoning Team (@SummoningTeam) exploited Canon imageFORCE 1643F Multifunction Copier with a bug chain of 4 unique bugs winning total of $5,000 and 2 Master of Pwn points
SUCCESS / COLLISION – Bye bye bridge @_McCaulay exploited the Philips Hue Bridge Pro winning $5,000 and 2 Master of Pwn points with a 4 bug collision #Pwn2Own
SUCCESS / COLLISION – $300,000!!!!! and 30 Master of Pwn points officially makes Ikotas Labs, Inc. the Master of Pwn as they jump to the top of the leader board after they chained multiple issues together to successfully exploit the Google Pixel 10 #Pwn2Own
SUCCESS – 2 unique bugs and down went the Lexmark CX532adwe as Cong Thanh (@ExLuck99), Duc Hieu (@gr4ss341) and Nam Dung (@greengrass19000) earned $5,000 and 2 Master of Pwn points in their successful exploit attempt #Pwn2Own
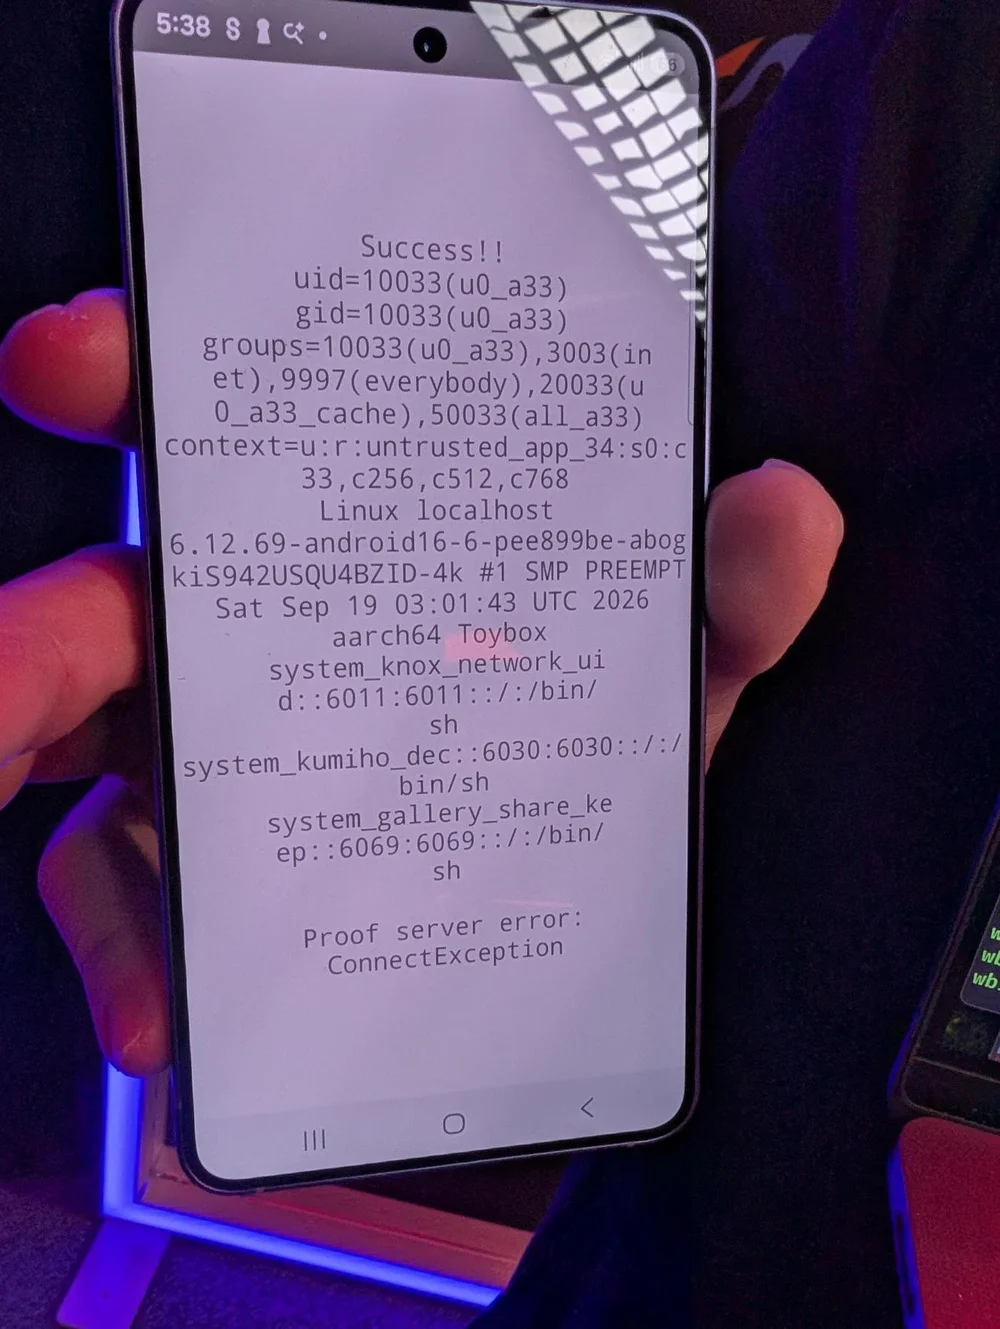
SUCCESS / COLLISION – Howdy Buckaroos, the very own BunkyoWesterns (@BunkyoWesterns) succeed in their remote lasso-ing of the Samsung Galaxy S26, with their 2 bug chain, 1 collission + 1 unique, earning them $8250 and 3.75 Master of Pwn points #Pwn2Own #P2OIreland
SUCCESS / COLLISION Booya! Cens-ational exploit by Dimitrios Valsamaras (@Ch0pin), Ken Gannon / 伊藤 剣 (@yogehi) using http://Djini.ai from Mobile Hacking Lab, Tenia Valsamara (@ir3l14) from CENSUS Labs targeting Google Pixel 10 – Remote in the Mobile Phone category for a total of $112,500 and 22.50 Master of Pwn points with a 2 bug chain, 1 collission and 1 zero-day #Pwn2Own
SUCCESS – A Mammoth of a bug chain of 6 zero days closes out #Pwn2OwnIreland by Chulhan Park, Mingeun Kim, SeokHun Lee, Inhyung Lee, Sehyun Baek, Nayeon Lee, Junseok Kim of Team MAMMOTH targeting Home Assistant Green in the Smart Home category for a total of $7500 and 3 Master of Pwn points #Pwn2Own
Day Two of Pwn2Own Ireland 2026 has 24 attempts on the docket, with roughly $780,000 up for grabs, running 9:30 AM to 7:30 PM IST.
Samsung’s Galaxy S26 will be attempted three separate times — by Valsamaras/Ken Gannon (using Djini.ai)/Valsamara at 1:00 PM, Kyeongmin Kim at 3:15 PM, and PetoWorks at 5:30 PM — worth watching since only the first successful demo claims the cash. Home Assistant Green is the day’s most-attempted device, with five researchers scheduled to take a run at it. AI Infrastructure stays active with four attempts on tap (Dynamo, two at Chroma, two at Oracle’s Autonomous AI Database), Wellness has just one attempt scheduled, and Printers see steady action with three separate attempts on the Lexmark CX532adwe.
Yesterday, we awarded $388,500 for 32 unique 0-days. Stay tuned for all of today’s results!
FAILURE – Unfortunately, the printers continue to be a challenge with Thanh Do (
@nyanctl
) of Team Confused unsuccessful in their targeting of Brother MFC-L8970CDW in the Printers category #Pwn2Own
SUCCESS – The grass may not be greener but the exploits sure were as Yves Bieri (@yves_bieri) of Xint (@xint_official) just won $30k and 3 Master of Pwn points in his takedown of Home Assistant Green #Pwn2Own
FAILURE – Another one bites the dust – with seconds left on the clock, unfortunately Eugene (
@k3vg3n
) targeting Chroma in the #AIInfrastructure category was unsuccessful in his final attempt #Pwn2Own
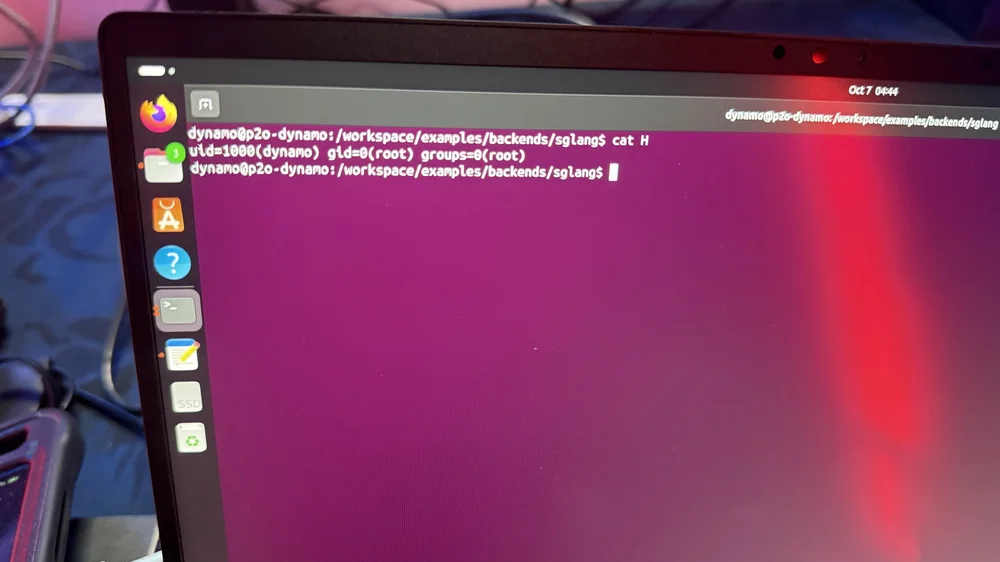
SUCCESS – A dynamite takedown of Dynamo in the AI Infrastructure category for a total of $40,000 and 4 Master of Pwn points by HaeJung Yang (@haehaeYang) of Out of Bounds (@oobs_io) #Pwn2Own
SUCCESS / COLLISION
We have another collision! Yassine Bengana (@cousky_), and Maxence Schmitt (@maxenceschmitt) of Doyensec (@doyensec) used 3 bugs to exploit the Home Assistant Green, but all 3 bugs were previously known. They still earn $7,500 and 1.5 Master of Pwn points. #Pwn2Own
SUCCESS –
Confirmed! @_McCaulay used 3 bugs (incl Hard-coded Credentials, Missing Authentication for Critical Function, Command Injection) to exploit the Canon imageFORCE 1643F. His 2nd round win nets him $10,000 and 2 Master of Pwn points. #Pwn2Own
SUCCESS / COLLISION –
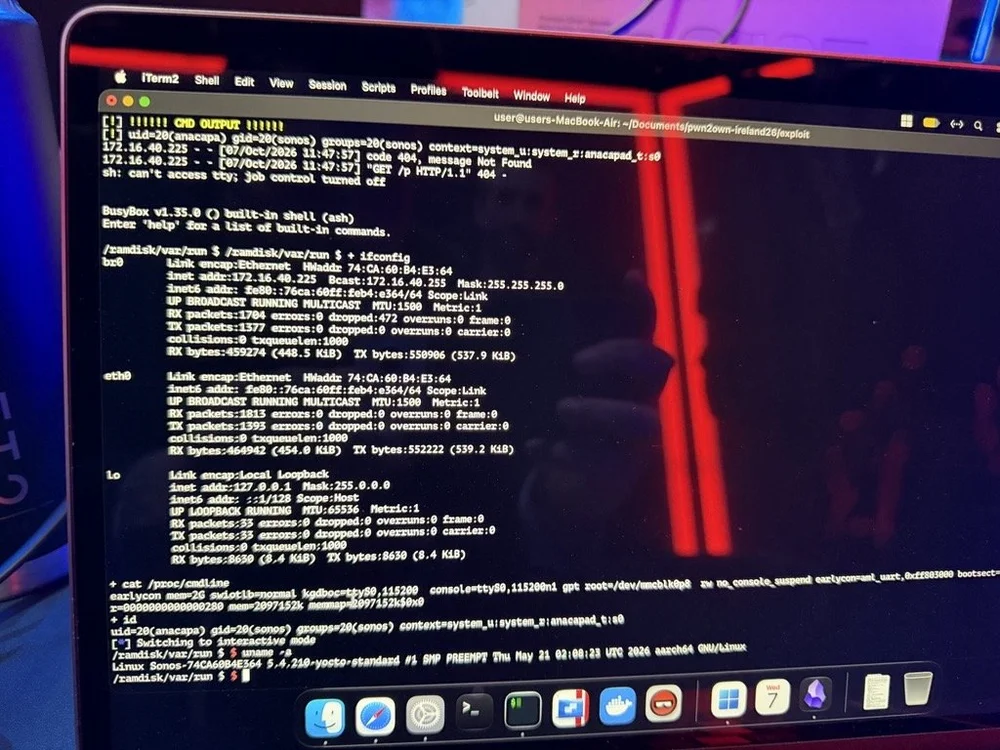
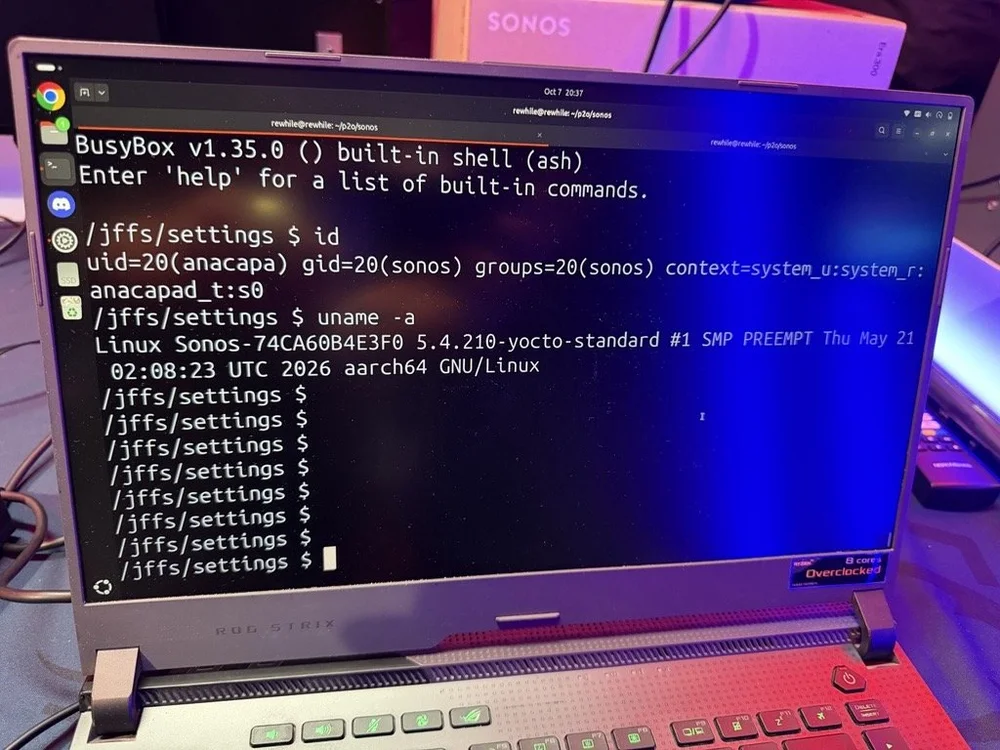
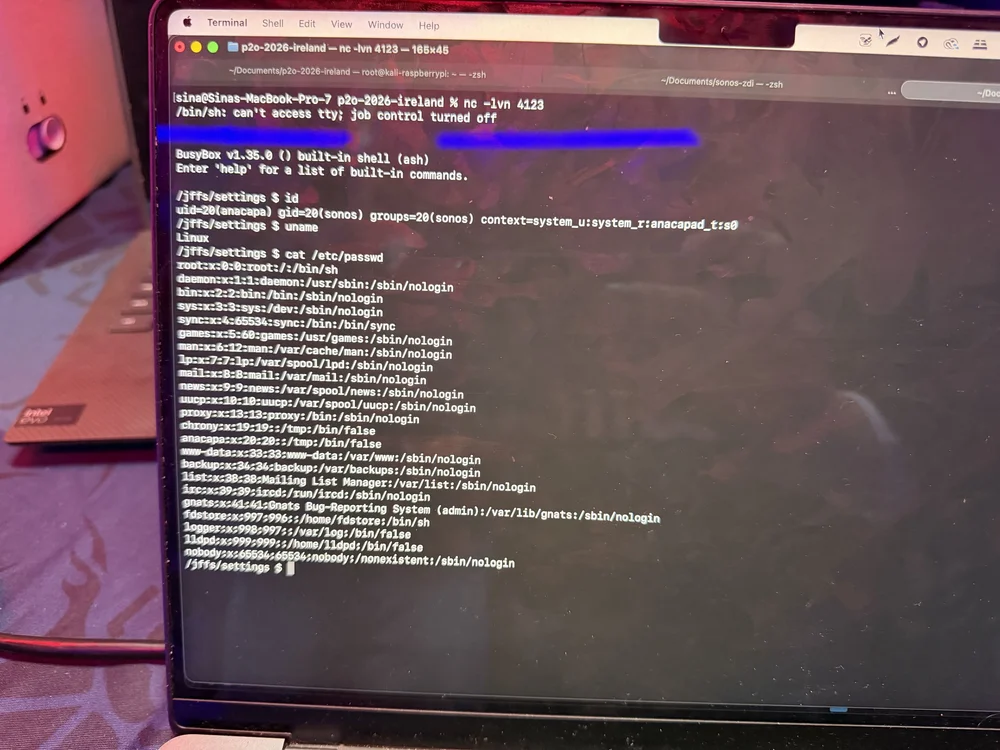
Against the clock in the final round…. Jack Dates of RET2 Systems (@ret2systems) locked in his win against the Sonos Era 300. The pot has been confirmed, with 1 zero day and 1 collision, he will take home $9.5K and 3.75 Master of Pwn points #Pwn2Own
SUCCESS / COLLISION – Boom! With 3 collisions and 2 unique zero-days Taisic Yun (
@taisic_
) of Xint (
@xint_official
) breached Oracle Autonomous AI Database capturing their pot of gold of $14k at #Pwn2OwnIreland and 3 Master of Pwn points #Pwn2Own
FAILURE – A valiant effort but Shio Kudo (
@shiosa1t
) of GMO Flatt Security Inc. (
@flatt_security
) was unsuccessful in their attempts at targeting Home Assistant Green in the Smart Home category #Pwn2Own
SUCCESS – 1 bug wonder! With an Confused Deputy (CWE-441) bug Dimitrios Valsamaras (@Ch0pin), Ken Gannon / 伊藤 剣 (@yogehi) using Djini.ai from Mobile Hacking Lab, Tenia Valsamara (@ir3l14) from CENSUS Labs PwN’ed the Samsung Galaxy S26 #Pwn2Own
SUCCESS / COLLISION – And the results are in! Nguyen Thanh Dat (@rewhiles), dungnm (@dungnm_) of Viettel Cyber Security (@vcslab) targeting Sonos Era 300 with 1 collision & 2 zero-days for a total of $10.5K and 4.25 Master of Pwn points #Pwn2Own
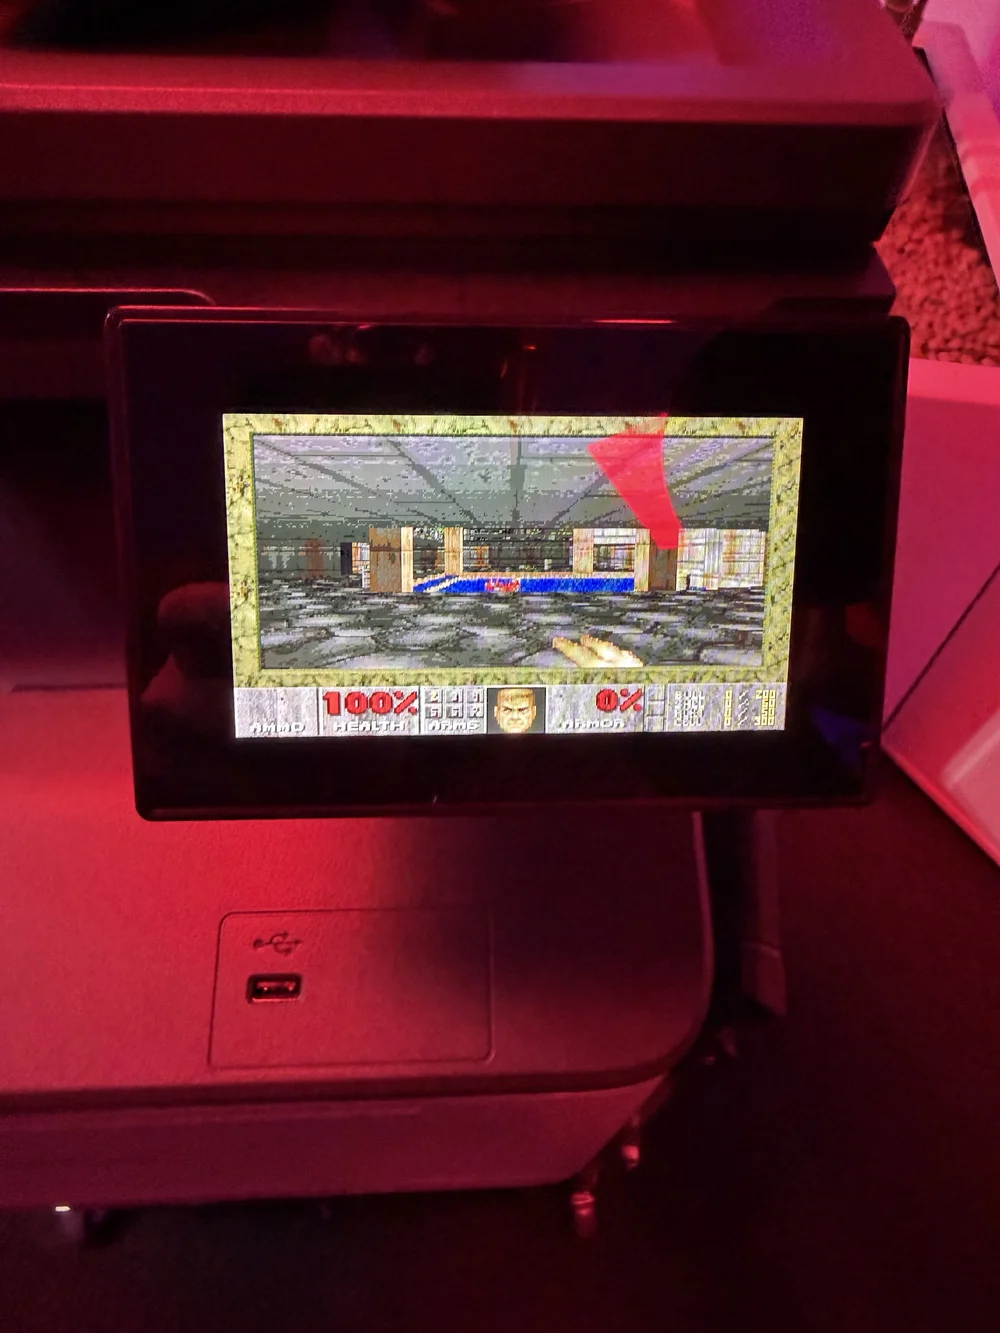
SUCCESS – It was DOOMsday for the Lexmark CX532adwe printer as Interrupt Labs (@InterruptLabs) claimed victory and earned $5k & 2 Master of Pwn points! #Pwn2Own #DoomHack
SUCCESS / COLLISION – Green means go! And boy did PetoWorks (@petoworks) go straight into the Home Assistant Green with a chain of 5 bugs including 2 collisions and 3 unique, securing $12k and 2.5 Master of Pwn points in the Smart Home category #Pwn2Own
SUCCESS / COLLISION – Direct connection – NOT needed for Kyeongmin Kim (@hareh4ru) of KAIST Hacking Lab who remotely breached the Samsung Galaxy S26 with 1 unique bug and 2 collision winning $8.5k and 3.5 Master of Pwn points #Pwn2Own
SUCCESS – Confused? Well Ikotas Labs, Inc. sure wasn’t as they unleased a 7-chain bug ending with a Use-After-Free and a Type Confusion on Oracle Autonomous AI Database securing a win of $10,000 and 4 Master of Pwn points #Pwn2Own
SUCCESS / COLLISION –
@_McCaulay climbs the leaderboard with his third target earning another 1.5 master of Pwn points and $6750 for his exploit of Garmin Index BPM with 1 collision and 1 unique bug.
SUCCESS / COLLISION – Confirmed! 1 zero-day & 3 collisions by Kyeongmin Kim (@hareh4ru) of KAIST Hacking Lab successfully exploited the Home Assistant Green in the Smart Home category earning him $4,750 and 2 Master of Pwn points #Pwn2Own
SUCCESS –
Another printer bites the dust by Rick de Jager and Filippo Cremonese of @zellic_io/@v12sec earning him $5k and 2 Master of Pwn points in his successful exploit of Lexmark CX532adwe #Pwn2Own
SUCCESS / COLLISION – Boom! With 3 bug collisions PetoWorks (@petoworks) successfully accessed the Samsung Galaxy S26 remotely, earning them a net $6250 and 2.5 Master of Pwn points #Pwn2Own
SUCCESS / COLLISION – A mammoth win by team MAMMOTH, with Mingeun Kim, Chulhan Park, SeokHun Lee, Inhyung Lee, Sehyun Baek, Nayeon Lee, Junseok Kim of Team MAMMOTH exploiting Chroma in the AI Infrastructure category with 2 collisions and 1 zero-day for a net total win of $12,000 and 1.25 Master of Pwn points #Pwn2Own
SUCCESS –
2 bugs + Sina Kheirkhah (@SinSinology) of Summoning Team = exploited Sonos Era 300 and $12,500 and 5 Master of Pwn points won! #Pwn2Own
SUCCESS / COLLISION – Exploit Confirmed!
@BoredPentester successfully exploited Lexmark CX532adwe in the Printers category with 1 collision & 2 unique bugs for a net total of $4250 and 1.25 Master of Pwn points #Pwn2Own
SUCCESS / COLLISION – @_McCaulay strikes again and down goes Home Assistant Green once again! With a 6 bug chain, including 1 collision and 5 zero-days, the net total winnings is $7k & 2.75 Master of Pwn points #Pwn2Own
SUCCESS / COLLISION – An impressive disclosure from Alessandro Fanio Gonzalez targeting Chroma with a 2 N-days & 1 collision in the AI Infrastructure category for a net total win of $4,500 and 1 Master of Pwn points #Pwn2Own
Potentially Unwanted Applications, or PUA, they aren’t necessarily malware, but they are applications you probably don’t want running across your environment either.Â
Microsoft defines potentially unwanted applications as software that can adversely affect endpoint performance or use. Examples include advertising software, software bundlers, and applications that use behaviors intended to evade security products. Microsoft Defender can also consider an application’s reputation when determining whether software qualifies as potentially unwanted.Â
That sounds straightforward.Â
On Windows, it generally is.Â
On Linux, finding the resulting audit events requires knowing exactly where to look.Â
And that is where things get interesting.Â
PUA, PUP… Same Neighborhood, Slightly Different AddressÂ
Before going further, it is worth clearing up some terminology.Â
Across the security industry, you will commonly encounter both PUP, or Potentially Unwanted Program, and PUA, or Potentially Unwanted Application. The terms are frequently used for software that isn’t necessarily malicious but has characteristics that make its presence undesirable, such as intrusive advertising, bundling additional software, or other behavior the user might not have knowingly requested.Â
Microsoft uses Potentially Unwanted Application (PUA) as its product and detection terminology.Â
Microsoft specifically distinguishes PUA from malware. A PUA might cause poor system performance, display unexpected advertisements, install other software, or have a poor reputation because of undesirable behavior, but those characteristics don’t automatically make the application malware.Â
Microsoft’s classification criteria include examples such as:Â
Advertising software that displays advertisements or promotions, including injecting advertisements into webpages.Â
Bundling software that offers to install additional software that isn’t digitally signed by the same entity, or that itself qualifies as PUA.Â
Evasion software that actively attempts to avoid detection by security products or behaves differently when security software is present.Â
Applications that have developed a poor reputation based on undesirable behavior.Â
Microsoft’s broader software-classification model also distinguishes between unknown software, malware, unwanted software, and other classifications. Software can therefore be legitimate and functional while still meeting Microsoft’s criteria for classification as potentially unwanted.Â
For the rest of this article, we’ll use PUA, because that is the terminology used by Microsoft Defender and, more importantly for our investigation, the Linux product logs identify these detections explicitly as:Â
potentially_unwanted_applicationÂ
That string is going to become very useful once we start looking for the supposedly elusive audit events.Â
PUA Audit and Block on WindowsÂ
On Windows, PUA protection is part of Microsoft Defender Antivirus. Administrators can configure Defender to identify applications that Microsoft considers potentially unwanted and determine how those applications should be handled.Â
Microsoft documents PUA protection and provides the AMTSO Potentially Unwanted Application test file (Feature Settings Check – Potentially Unwanted Applications – AMTSO)Â as its standard demonstration scenario. Microsoft’s demonstration documentation identifies Windows, Windows Server, macOS, and Linux among the supported operating systems for the PUA demonstration.Â
The two operating modes we’re interested in are conceptually simple:Â
AuditÂ
Defender identifies the PUA but doesn’t block it. This is useful when you want to understand the potential impact of enabling PUA protection before enforcing it.Â
BlockÂ
Defender identifies the PUA and takes the configured protection action.Â
On Windows, for a device onboarded to Microsoft Defender for Endpoint – that telemetry and audit information is available in the XDR Security portal. You can find PUA detections in the Additional Fields of the AntivirusDetection action type in the DeviceEvents table – and an alert will fire when in PUA is in block mode:Â
Microsoft Defender Antivirus events can be investigated through:Â
Applications and Services Logs > Microsoft > Windows > Windows Defender > OperationalÂ
Defender detection events can provide information such as the threat name, threat ID, category, path, detection origin, detection type, and detection source.Â
That makes auditing and troubleshooting reasonably familiar territory for Windows administrators.Â
The experience on Linux, however, is different.Â
PUA Protection on LinuxÂ
Microsoft Defender for Endpoint on Linux also supports PUA protection.Â
Microsoft documents three PUA actions:Â
Off: PUA protection is disabled.Â
Audit: PUA files are reported in the product logs, but no remediation is performed.Â
Block: PUA files are reported and action is taken against them.Â
The distinction between Audit and Block is particularly important.Â
In PUA Audit mode:Â
PUA files are reported in the product logs.Â
They aren’t reported in the Defender portal through this PUA mechanism.Â
No infection record is stored in threat history.Â
No action is taken against the file.Â
In Block mode:Â
The detection is reported in the product logs.Â
It is reported in the Defender portal.Â
A record is stored in threat history.Â
Defender takes action on the PUA.Â
PUA behavior can be configured locally with mdatp.Â
To configure Audit:Â
sudo mdatp threat policy set –type potentially_unwanted_application –action auditÂ
To configure Block:Â
sudo mdatp threat policy set –type potentially_unwanted_application –action blockÂ
There is one important distinction worth calling out here: PUA Audit mode isn’t the same thing as the broader Microsoft Defender for Endpoint Antivirus Passive Mode on Linux.Â
PUA Audit is specifically the handling policy for applications that are detected and classified as potentially unwanted.Â
For this article, we’re testing and focusing on PUA Audit.Â
A Windows PUA on Linux? Yes.Â
Here’s where the test gets more interesting.Â
The AMTSO PUA test artifact is a Windows executable. At first glance, that doesn’t seem particularly useful when we’re trying to validate PUA protection on Linux.Â
After all, we’re testing on Linux.Â
But Defender’s file inspection isn’t limited to applications that can execute natively on the operating system. A Windows PE file sitting on a Linux filesystem can still be inspected and classified.Â
And we can demonstrate that directly.Â
Microsoft’s PUA demonstration directs administrators to the AMTSO Potentially Unwanted Application test file, and Microsoft’s current demonstration documentation includes Linux among the supported operating systems.Â
On our Linux test machine, we downloaded:Â
PotentiallyUnwanted.exeÂ
The important point is that we don’t need to execute the Windows executable on Linux.Â
In our testing, simply causing filesystem activity against the file was sufficient to make Defender inspect it.Â
The file initially resided in:Â
/home/ritter/Downloads/PotentiallyUnwanted.exeÂ
We then used the Linux graphical file manager to move it into:Â
/home/ritter/Music/PotentiallyUnwanted.exeÂ
That was enough to generate another PUA Audit observation.Â
The Defender record showed:Â
“scan_reason”:”move”Â
And, more importantly, Defender classified the file as:Â
“name”:”PUA:Win32/EICAR_Test_File”Â
with:Â
“type”:”potentially_unwanted_application”Â
and:Â
“status”:”infected”Â
The event also recorded information about the process responsible for the filesystem operation. In our test, moving the file graphically resulted in the process being recorded as:Â
/usr/bin/nautilusÂ
So although the test artifact is a Windows executable, MDE running on Linux still inspected and classified it asPUA:Win32/EICAR_Test_File.Â
That’s exactly what we needed.Â
So Where Is the Audit Event?Â
This is the elusive part.Â
If you immediately start looking in the Defender portal or expect PUA Audit to behave like PUA Block, you’re likely to come away wondering whether anything happened.Â
Microsoft’s Linux documentation tells us that Audit-mode PUA files are reported in the product logs and that no infection record is stored in threat history.Â
Fair enough.Â
But that naturally leads to another question:Â
Which product log?Â
Instead of guessing, we asked Linux.Â
A recursive grep across the MDE log directory provides a simple way to find anything containing the PUA classification string:Â
The PUA audit event exists. You just have to go spelunking through the local Defender product logs to find it.Â
The Microsoft documentation is technically correct: PUA Audit detections are written to the product logs.Â
Knowing what string to search for and which log actually contained the events on our test system makes that guidance considerably more actionable.Â
That’s Fine for One Server. What About 1,000?Â
Running grep on a test machine is easy.Â
Running grep individually across hundreds or thousands of Linux servers obviously isn’t the operational model we want.Â
Once we know where the information resides, however, the problem changes from a Defender problem into a log collection problem.Â
And that’s a much easier problem to solve.Â
One option is Azure Monitor Agent (AMA).Â
AMA supports collecting custom text logs from Linux systems through an Azure Monitor Data Collection Rule (DCR) and sending those records to a Log Analytics workspace.Â
Conceptually:Â
Â
Â
Â
A DCR can be configured to collect the Defender text log identified during testing. Azure Monitor supports Linux custom-text-log file patterns and wildcards for appropriate log-file collection scenarios.Â
Azure Monitor Custom Text Logs also supports ingestion-time transformations, allowing records to be filtered or formatted before they’re written to the destination table.Â
That creates an interesting opportunity.Â
Rather than collecting every line from a verbose Defender diagnostic log, a collection strategy could focus on the records containing:Â
potentially_unwanted_applicationÂ
Once centralized in Log Analytics, those records become queryable with KQL.Â
For example, if the records were ingested into a custom table called MDEPUAAudit_CL, an initial investigation could start with:Â
MDEPUAAudit_CLÂ
| where RawData contains “potentially_unwanted”Â
From there, the raw records could be parsed for useful reporting fields including:Â
HostÂ
TimestampÂ
File pathÂ
Detection nameÂ
PUA classificationÂ
Scan reasonÂ
Initiating processÂ
First occurrenceÂ
Last occurrenceÂ
Number of observationsÂ
Â
Turning Audit Mode into a Deployment ToolÂ
This is ultimately where the exercise becomes useful.Â
PUA Audit doesn’t have to be merely a configuration checkbox. It can become a pre-enforcement assessment mechanism.Â
The workflow looks something like this:Â
Â
Â
Â
Instead of asking:Â
“What happens if we turn PUA Block on?”Â
we can start answering a much better question:Â
“What has Defender already identified as PUA while we’ve been running in Audit?”Â
And now we know where the answer is hiding.Â
ReferenceÂ
Live linkÂ
Detect and block potentially unwanted applications with Microsoft Defender for Endpoint on LinuxÂ
Update:The Windows 11, version 26H2 security baseline has been updated to reflect the general availability of Administrator protection. An updated v2 package is now available, and organizations should review and test the existing Administrator protection configuration as appropriate for their environment.
Â
You can download the baseline package from the Microsoft Security Compliance Toolkit, test the recommended configurations in your environment, and customize / implement them as appropriate.
Summary of Changes
This release includes several changes since the Security baseline for Windows 11, version 25H2 to further strengthen enterprise security and align the baseline with current platform capabilities and industry standards.
Security Policy
Change Summary
Printer\Configure Windows Ready Print driver ranking
Configured as “Enabled†to reduce reliance on third-party print drivers in the stack, narrowing the overall print driver attack surface.
Internet Explorer\Internet Control Panel\Advanced Page\Turn off encryption support
Updated from TLS 1.1 and TLS 1.2 to TLS 1.2 and TLS 1.3 to align with current security standards.
User Account Control: Configure type of Admin Approval Mode (updated)
Configured as “Admin Approval Mode with Administrator protection†to enable Administrator protection.
User Account Control: Behavior of the elevation prompt for administrators running with Administrator protection (updated)
Configured as “Prompt for credentials on the secure desktop†to require credential verification for administrative elevation.
Â
Windows Ready Print driver ranking
Configure Windows Ready Print driver ranking” is the newly added setting under Administrative Templates\Printers to control whether Windows prefers the modern inbox IPP class driver over third-party OEM drivers when installing new printers. We recommend enabling this policy to reduce reliance on third-party print drivers in the stack, narrowing the overall print driver attack surface. Note that driver ranking applies when printers are installed via a connection method that supports IPP, such as USB or network multicast discovery. In those cases, if the printer supports IPP, Windows will install using the class driver even if a vendor V3/V4 driver is available. If the printer doesn’t support IPP, or is installed directly as a TCP/IP printer, there’s no change in behavior.
Â
Encryption Support
We have updated the policy “Turn off encryption support” to allow only TLS 1.2 and TLS 1.3. Previous baseline releases permitted TLS 1.1 and TLS 1.2; however, TLS 1.1 is now considered obsolete and is no longer recommended for enterprise environments. This change aligns the security baseline with modern cryptographic standards while maintaining compatibility with widely deployed services that support current TLS versions.
Â
Administrator Protection (update)
Administrator protection is now generally available. Organizations can enable it through Microsoft Intune or Group Policy.
Important: Organizations should review and test their existing configuration and adjust these settings as appropriate for their environment. The security baselines for Windows 11, versions 24H2, 25H2, and 26H2 include settings that enable Administrator protection.
The following policies are part of the security baseline:
User Account Control: Configure type of Admin Approval Mode
User Account Control: Behavior of the elevation prompt for administrators running with Administrator protection
An updated v2 package has been published for Windows 11, version 26H2, to reflect this change.
Email remains one of the most common entry points for security threats. Yet email products often describe the same activity with different table names, fields, and values. This makes it harder to build detections and investigations that work consistently across data sources.
The Microsoft Sentinel Advanced Security Information Model, or ASIM, EmailEvent schema is now available. It provides a common structure for email delivery and inspection events, helping customers and partners create security content that works across supported email data sources.
A consistent view of email security activity
EmailEvent standardizes the information analysts need to understand what happened to an email and why. It covers:
Email delivery and inspection eventsÂ
Sender, source, and recipient informationÂ
Message subject, size, direction, and delivery locationÂ
URLs and file attachmentsÂ
SPF, DKIM, and DMARC authentication resultsÂ
Delivery actions such as delivered, blocked, quarantined, or deletedÂ
Threat, risk, confidence, tactic, technique, and remediation detailsÂ
Instead of learning a different data model for every product, analysts can query the normalized EmailEvent fields. Parser developers map each source’s native data to the same schema.
How it works
Consider an email that contains a suspicious attachment. The email security product records the sender, recipients, attachment, authentication results, inspection verdict, and final action. A connector collects that event. A parser or Data Collection Rule maps the source fields to EmailEvent. Microsoft Sentinel can then query the normalized record using the same field names used for other supported email sources.
This common structure separates security content from the details of a specific product. When another source adds an EmailEvent parser, existing source-independent queries and detections can work with that source without being rewritten around its native field names.
Why it matters
Simpler analytics: Write queries against one consistent set of email fields.Â
Broader coverage: Apply source-independent security content across normalized email sources.Â
Faster investigations: Compare delivery, authentication, attachment, URL, and threat details without translating different data models.Â
Easier integration: Give connector and parser developers a defined contract for bringing new email telemetry into ASIM.Â
EmailEvent does not replace the rich native data produced by email security products. It provides a consistent security layer that makes that data easier to use together.
Build on EmailEvent
The EmailEvent release includes the schema definition, source-independent parser framework, filtering parser, deployment templates, and validation support in the Azure-Sentinel repository. The schema version is 1.0.0.
Customers can use normalized EmailEvent data to develop hunting queries, analytics rules, workbooks, and investigation experiences. Partners and community contributors can create source-specific parsers that map their email data to the schema.
Thank you to the ASIM engineering and partner teams who contributed to the schema, deployment path, validation, and release.
Content on this page is collected from remote sources by IPWorX but is not created by IPWorX. The contents belong to the creators and should be considered theirs for all legal purposes, we have no editorial control or responsibility over them. IPWorX does not represent or endorse the accuracy or reliability of any opinion, statement, or other information provided by any third party.
This page contains links to third-party websites. These links are provided solely for your convenience. IPWorX does not control, maintain, or endorse the content, accuracy, or reliability of any third-party resources, and you access them at your own risk.
Scripts and tools to help manage your network found, managed and
happily shared with documentation on usage at the IP WORk eXchange.
https://www.IPWorX.com